
The most effective approach for U.S. blockchain startups is a lawyer-led, risk-based KYC and sanctions compliance program (SCP) built on OFAC’s five-component framework, documented internal controls, and auditable casework. This is not a software selection problem. It is a legal program design problem, and the consequences of getting it wrong include civil monetary penalties, blocked property reporting failures, and personal liability for compliance officers.
Your 72-hour triage list:
- Confirm whether your business qualifies as a money services business (MSB) under FinCEN rules and register if required
- Verify that your sanctions screening covers wallet-level controls, not just name matching
- Log any known red-flag counterparties and preserve those records immediately
- Confirm your audit trail captures how every alert was handled and every decision was reached
OFAC’s framework requires blocked property to be reported within 10 business days. FinCEN’s Bank Secrecy Act (BSA) obligations require Suspicious Activity Reports (SARs) within 30 days of detection. Neither deadline is forgiving, and neither regulator accepts “we were still building the program” as a defense.
Pro Tip: Preserve immutable snapshots of on-chain transaction data and analyst notes from day one. Evidence that cannot be reconstructed later is evidence that does not exist in an enforcement proceeding.
Key Takeaways
A lawyer-led, risk-based KYC and sanctions compliance program built on OFAC’s five components, with auditable controls and documented vendor oversight, is the defensible standard for U.S. blockchain startups.
| Point | Details |
|---|---|
| OFAC reporting deadline | Blocked property must be reported within 10 business days; an effective SCP can mitigate civil penalties. |
| SAR filing windows | Initial SARs are due within the regulatory deadline; continuing SARs must be filed if activity persists; records must be retained per regulatory requirements. |
| Five program components | Management commitment, risk assessment, internal controls, testing/auditing, and training are all required. |
| Auditability is the differentiator | Every alert disposition and SAR decision must be documented; template policies without evidence of use do not qualify. |
| Murphyslawcrypto | Offers compliance program design, vendor contract review, CCO training, and regulatory defense with enforcement litigation experience. |
Table of Contents
- What does a defensible KYC/SCP checklist look like for blockchain startups?
- How do OFAC, FinCEN, and the SEC create overlapping KYC obligations?
- What are the five core components every blockchain startup’s SCP must include?
- Which KYC signals actually matter beyond name screening?
- What must your KYC vendor contracts actually say?
- How should you handle a screening hit or suspicious activity alert?
- How do you choose legal counsel to design and defend your KYC program?
- What program failures actually trigger enforcement actions?
- Which KYC software tools work best for blockchain startups?
- What data privacy and security practices does your KYC program require?
- How do you deploy a KYC/SCP from scratch in a blockchain startup?
- Why a law firm should lead your KYC program design
- Murphy’s Law offers compliance program design built for enforcement defense
- Sources
- FAQ
What does a defensible KYC/SCP checklist look like for blockchain startups?
A one-page checklist your founder or Chief Compliance Officer (CCO) can use to validate program coverage:
- Management commitment: Written policy signed by a senior officer; designated CCO with documented authority
- Risk assessment: Customer risk tiers, product risk matrix, geographic risk scoring updated at least annually
- Customer Due Diligence (CDD): Identity verification, beneficial ownership collection, enhanced due diligence (EDD) triggers for high-risk counterparties
- Sanctions screening: Name screening plus wallet-level controls; documented screening logic and override procedures
- Transaction monitoring: Typology-based alert rules; documented alert disposition with analyst sign-offs
- SAR and OFAC reporting: 30-day SAR filing window; 10-business-day blocked property reporting; 90-day continuing SAR cadence
- Vendor oversight: Contracts with SLA, audit rights, and data retention clauses
- Training: Annual AML/sanctions training with attendance records
- Testing and audit: Independent audit at least annually; remediation tracking
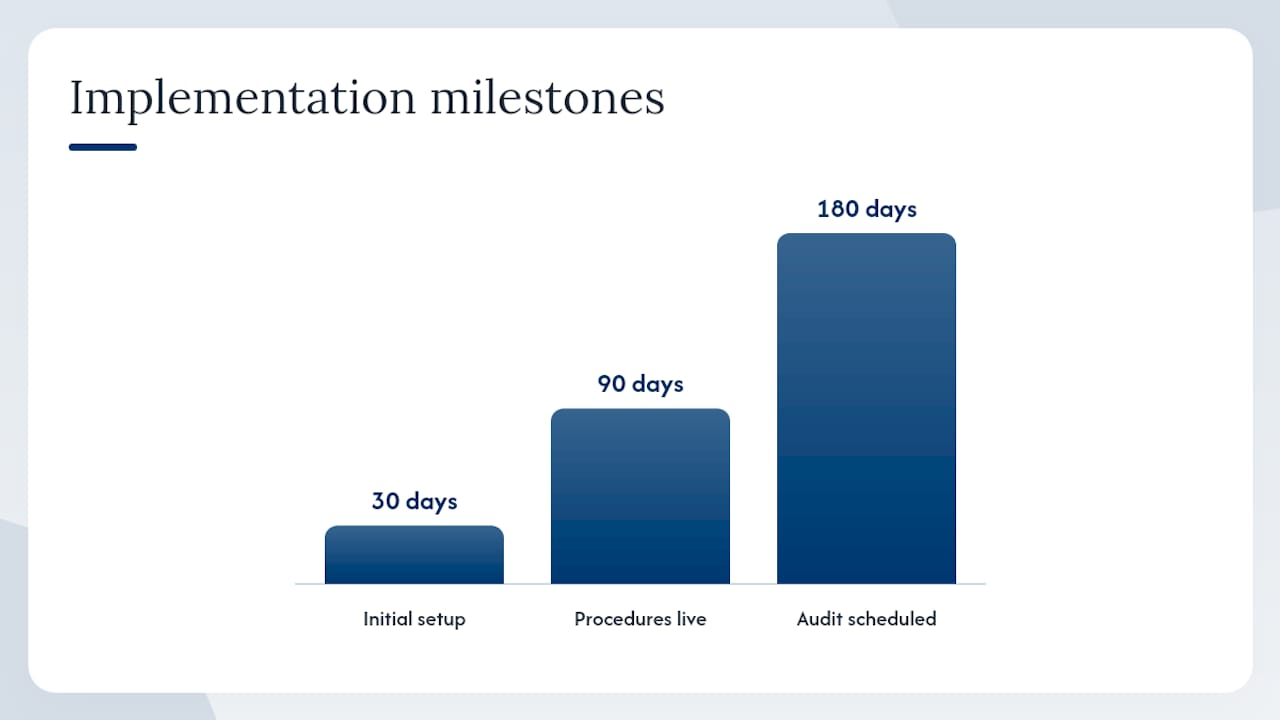
Implementation milestones:
- 30 days: MSB registration confirmed, CCO designated, written policy drafted, screening logic documented
- 90 days: Risk assessment complete, CDD procedures live, vendor contracts reviewed, first training delivered
- 180 days: Independent audit scheduled, SAR procedures tested, remediation log established
Call counsel immediately if: you have received a regulatory inquiry, you have identified a potential blocked property situation, or your screening has produced alerts you cannot disposition with confidence. Early regulatory counsel reduces both remediation cost and enforcement exposure.
How do OFAC, FinCEN, and the SEC create overlapping KYC obligations?
OFAC, FinCEN’s BSA framework, and the SEC create three distinct but overlapping compliance obligations. A program designed to satisfy only one will leave gaps the others can exploit.
- FinCEN/BSA: MSBs and exchanges must file SARs within a regulatory deadline after detecting suspicious activity. Continuing SARs are required if the activity persists. Records must be retained for a regulatory period.
- SEC: Enforcement posture toward compliance officers has hardened. Practical Law/Reuters analysis notes that SEC officials have signaled enforcement against compliance personnel where there is a wholesale failure to carry out responsibilities. Documented, proactive programs are the primary defense.
U.S. crypto operators also carry licensing obligations that vary by state, adding a multistate compliance layer that program design must account for from the start.
For SAR filing specifics including thresholds, documentation expectations, and continuing SAR procedures, consult primary FinCEN guidance and firm resources before your first filing.
What are the five core components every blockchain startup’s SCP must include?
OFAC’s framework identifies five components. Each maps directly to KYC program elements a startup can implement:
| Component | KYC/SCP Artifact |
|---|---|
| Management commitment | Signed compliance policy; CCO appointment letter |
| Risk assessment | Customer and product risk matrix; geographic risk tiers |
| Internal controls | CDD procedures; wallet screening logic; monitoring alert rules |
| Testing and auditing | Independent audit report; remediation log |
| Training | Annual training curriculum; attendance and completion records |
The process flow runs: onboarding → monitoring → alert triage → investigation → escalation → report or close. Every handoff point must create a documented record. Analysts must sign off on dispositions. Legal review triggers must be written into the escalation procedure, not left to judgment.
Bank-grade KYC/KYB is now the baseline expectation. Weak onboarding and missing documentation are the most common failure points in enforcement actions.
Pro Tip: When building automated monitoring, capture the logic version and threshold settings in a dated configuration log. Regulators will ask what your system was set to at the time of a specific transaction, and “we updated it since then” is not an answer.
Which KYC signals actually matter beyond name screening?
Name screening alone is insufficient. Wallet-level analysis, IP/geolocation, transaction typologies, and counterparty risk are required signals for a defensible program.
Signal types and what each catches:
- Wallet-level screening: Identifies addresses linked to sanctioned entities, mixers, or darknet markets; limited by address clustering accuracy
- IP/geolocation: Flags connections from sanctioned jurisdictions or VPN/Tor exit nodes; requires documented override logic for false positives
- Transaction typologies: Rapid cycling, layering, structuring, and peer-to-peer patterns that suggest deliberate obfuscation
- Counterparty risk: Exposure to high-risk exchanges, unhosted wallets, or jurisdictions with weak AML regimes
Investigation workflow: Automated flag → analyst triage (accept, escalate, or close with notes) → supervisor review for escalated cases → legal review trigger for potential SAR or blocked property → documented decision with evidence preserved.
Every step must produce a written record. The ability to show how every alert was handled is what separates a defensible program from a template that exists only on paper.
Pro Tip: Measure your false positive rate and SAR conversion rate quarterly. A false positive rate above 95% signals miscalibrated rules; a SAR conversion rate near zero signals alerts are being closed without genuine analysis.
What must your KYC vendor contracts actually say?
Outsourcing KYC functions is acceptable. Outsourcing compliance responsibility is not. The startup retains full regulatory accountability regardless of what a vendor does or fails to do.
Required contract provisions:
- Service level agreements with defined uptime and accuracy benchmarks
- Audit rights allowing the startup (and its counsel) to inspect vendor processes and data
- Data retention terms matching or exceeding the five-year BSA requirement
- Subprocessor disclosure and approval rights
- Escalation procedures for potential blocked property or SAR-triggering events
- Termination triggers tied to compliance failures or audit findings
Oversight cadence:
- Monthly: Review vendor KPIs against SLA benchmarks
- Quarterly: Sample vendor alert dispositions and test case results
- Annually: Commission an independent assessment of vendor performance
Vendor contracts should also specify which party is responsible for filing reports when a vendor-generated alert becomes a reportable event. Ambiguity on that point has produced enforcement failures.
Pro Tip: Run test cases through your vendor’s screening system at least quarterly. Use known-bad wallet addresses and synthetic customer profiles to confirm the system flags what it should.
How should you handle a screening hit or suspicious activity alert?
Follow a documented investigation playbook. Every alert must create an auditable chain from detection to resolution.
Investigation checklist:
- Confirm identity verification records are complete and current
- Pull on-chain transaction history for the relevant address or counterparty
- Document counterparty risk notes, including any adverse media or watchlist hits
- Record analyst sign-off with timestamp and rationale
- Trigger legal review if the alert involves a potential OFAC match or SAR threshold
Pro Tip: Document false positives as thoroughly as true positives. A regulator reviewing your program will look at how you closed alerts, not just how you filed reports. Thin false-positive records suggest the analysis was not done.
How do you choose legal counsel to design and defend your KYC program?
Hire counsel with both enforcement defense experience and compliance program design capability. A firm that has only drafted policies but never defended them in an enforcement setting cannot tell you whether your documentation will hold up.
Questions to ask shortlisted firms:
- What OFAC and FinCEN enforcement matters have you defended, and what were the outcomes?
- Have you designed and audited KYC programs for crypto businesses at our stage?
- Can you draft and review vendor contracts for outsourced compliance functions?
- Do you provide CCO training, and can you support an independent audit?
- If we receive a regulatory inquiry, what is your response protocol and timeline?
Red flags: No enforcement history, template-only policy packages, unwillingness to support audits, and no documented remediation examples from prior engagements.
Engagement typically runs in three phases: initial assessment (weeks 1 to 4), program build (weeks 5 to 12), and ongoing retainer for regulatory response. Crypto executive personal liability is a real and growing risk; counsel who understands that dynamic will build documentation with enforcement defense in mind from the start.
Murphyslawcrypto, led by Liam Murphy, Esq. (Penn Law, formerly Paul Hastings, Selendy Gay, and McKool Smith), brings litigation experience from matters involving Celsius, Terraform Labs, and BitMEX. That enforcement background shapes how the firm designs compliance programs, because the documentation that survives a regulator’s review is built differently than documentation that only satisfies an internal checklist.
What program failures actually trigger enforcement actions?
The most common root causes are weak onboarding, poor documentation, insufficient sanctions controls, absent audit trails, and inadequate vendor oversight. These are not hypothetical risks.
- Weak onboarding: Missed beneficial owners, incomplete identity verification, and no EDD for high-risk counterparties
- Insufficient sanctions controls: Name-only screening that misses wallet-level exposure; no documented override logic
- Poor documentation: Alert dispositions with no analyst rationale; SAR decisions that cannot be reconstructed
- Absent audit trails: No record of what the monitoring system was configured to catch at a given point in time
- Vendor failures: Outsourced functions with no audit rights, no SLA enforcement, and no escalation path
Enforcement settlements consistently show that regulators reduce penalties when a business can demonstrate a documented, functioning compliance program at the time of the violation and a credible remediation plan afterward. The program does not need to have been perfect. It needs to have been real, documented, and actively maintained. Template policies with no evidence of implementation do not qualify.
Which KYC software tools work best for blockchain startups?
The KYC software category for blockchain startups includes identity verification platforms, document and biometric checks, sanctions screening engines, and blockchain analytics tools. The right combination depends on your customer base, transaction volumes, and risk tier.
When evaluating tools, prioritize: API integration depth with your onboarding stack, wallet-level screening coverage (not just name lists), audit log export capability, and vendor willingness to support your compliance team’s investigation workflow. Pricing models vary widely, from per-verification fees to monthly platform subscriptions, and most enterprise-grade tools require direct negotiation.
No tool replaces the legal program design layer. Software generates alerts; your documented procedures determine what happens next. A well-configured tool running under a weak program produces alerts that go nowhere. A well-designed program running under a basic tool produces defensible casework.
What data privacy and security practices does your KYC program require?
KYC data is among the most sensitive personal information a blockchain startup collects. U.S. state privacy laws, including the California Consumer Privacy Act (CCPA) and its amendments, impose obligations on how that data is collected, stored, and shared.
Core practices: collect only what your risk assessment requires, store KYC records in encrypted systems with access controls, define retention periods that meet the five-year BSA floor without exceeding what privacy law permits, and document your data handling procedures in your compliance policy. Vendor contracts must address data residency, breach notification timelines, and deletion rights.
Blockchain startups that operate internationally face additional obligations under frameworks such as the EU’s General Data Protection Regulation (GDPR). If your customer base includes EU residents, your KYC data handling procedures need a separate legal review.
How do you deploy a KYC/SCP from scratch in a blockchain startup?
A phased implementation roadmap keeps the program defensible at every stage, even before it is complete.
Phase 1 (Days 1 to 30): Designate a CCO, confirm MSB registration status, draft a written compliance policy signed by a senior officer, document your screening logic, and preserve all existing customer records.
Phase 2 (Days 31 to 90): Complete your risk assessment, build CDD and EDD procedures, review and revise vendor contracts, deliver first-round training, and establish your SAR and OFAC reporting procedures in writing.
Phase 3 (Days 91 to 180): Commission an independent audit, test your monitoring alert rules with known typologies, establish a remediation log, and schedule your first continuing SAR review cycle.
At each phase, the program should be documented well enough that a regulator reviewing it at that moment could see a functioning, good-faith compliance effort. Partial programs that are clearly in progress fare better in enforcement than programs that appear to have never started.
Why a law firm should lead your KYC program design
Most KYC program failures are not technology failures. They are documentation failures. The policies exist, the tools are running, but the written procedures do not match what the tools actually do, the escalation triggers are not defined, and the audit trail does not show how decisions were reached. When a regulator arrives, those gaps are the story.
Lawyers frame compliance policies with enforcement defense in mind from the first draft. Legal reporting triggers are integrated into the escalation procedure, not added later. The documentation is built to answer the questions a regulator will ask, because counsel who has defended enforcement matters knows exactly what those questions are.
Murphyslawcrypto’s crypto compliance consulting practice is built on that principle. Liam Murphy, Esq. has litigated high-profile matters involving Celsius, Terraform Labs, and BitMEX. That litigation background is not incidental to compliance program design. It is the reason the firm’s programs are built to survive scrutiny, not just satisfy an internal checklist.
Startups should escalate from in-house counsel to external regulatory defense counsel when they receive a government inquiry, identify a potential blocked property situation, or discover a compliance gap that predates the current program. At that point, the documentation you have already built determines how the matter resolves.
Murphy’s Law offers compliance program design built for enforcement defense
A compliance program that looks good on paper but cannot survive a regulatory review is a liability, not an asset. Murphyslawcrypto designs KYC and sanctions compliance programs for U.S. blockchain startups with enforcement defense built in from the start, not retrofitted after a problem surfaces.
The firm offers fixed-fee initial assessments, phased program builds covering policy drafting, vendor contract review, CCO training, and independent AML audits, and retainer arrangements for ongoing regulatory response. Liam Murphy, Esq. and the team bring direct litigation experience from some of the most significant enforcement matters in the crypto space, which means the documentation they build reflects what regulators actually scrutinize.
If your program is incomplete, untested, or has never been reviewed by counsel with enforcement experience, the time to address that is before a regulator asks. Review the firm’s crypto compliance program services and schedule a compliance assessment.
Sources
Primary government and trusted legal sources for U.S. blockchain startup KYC compliance:
- Crypto Compliance: Key Considerations | Practical Law The Journal | Reuters
- Crypto Business Compliance: U.S. Licensing and Regulations | Carlton Fields
This article is general information, not a substitute for advice from a qualified lawyer. Consult a qualified legal professional about your own circumstances before acting on anything here.
FAQ
What is the 10-business-day OFAC reporting rule?
When a blockchain startup blocks property belonging to a sanctioned person or entity, it must report that blocked property to OFAC within 10 business days. Failure to report on time is itself a potential violation.
Do all crypto startups need to file SARs?
MSBs and exchanges registered with FinCEN are required to file SARs for suspicious transactions above applicable thresholds. The initial SAR is due within 30 days of detection, with continuing SARs every 90 days if the activity continues.
What makes a KYC program “defensible” in an enforcement context?
A defensible program documents how every alert was handled, every SAR decision was reached, and every vendor was overseen. Template policies with no evidence of implementation do not satisfy regulators.
When should a blockchain startup hire external compliance counsel?
Hire external counsel before your program is built, not after a problem surfaces. Early regulatory counsel reduces both remediation cost and enforcement exposure, particularly for startups approaching their first audit or regulatory inquiry.
Can Murphyslawcrypto design a KYC program for a crypto startup?
Yes. Murphyslawcrypto offers compliance program design, vendor contract review, CCO training, independent AML audits, and regulatory defense, with litigation experience from high-profile enforcement matters including Celsius, Terraform Labs, and BitMEX.