
A defensible compliance program for a crypto startup rests on three actions taken in the first weeks of operation: register as a money services business with FinCEN and treat the Bank Secrecy Act as your floor, appoint a named compliance owner with real authority, and complete a one-page AML and sanctions risk assessment. Everything else, from Know Your Customer (KYC) tiers to Travel Rule vendors, builds on that foundation in stages rather than all at once.
TL;DR:
- Register as a money services business with FinCEN and complete a one-page AML and sanctions risk assessment within the first weeks of operation.
- Know if your platform qualifies as an MSB or needs state licensing based on activities like holding customer funds or facilitating transfers, and prepare necessary compliance documentation accordingly.
- Build and document seven core controls, including risk assessments, governance, tiered KYC onboarding, transaction monitoring, sanctions screening, SAR workflows, and Travel Rule readiness, scaling them as your volume grows.
- Track key metrics such as onboarding rejection rates, alert volume, false positive rates, and time-to-close to demonstrate your program functions effectively during audits or exams.
- View compliance as an essential infrastructure component that enables banking relationships and regulatory trust, not just a cost or paperwork, with preparedness for regulator and bank inquiries.
Table of Contents
- What Regulatory Perimeter and Obligations Apply to Your Crypto Startup
- Core Components of a Crypto Compliance Program
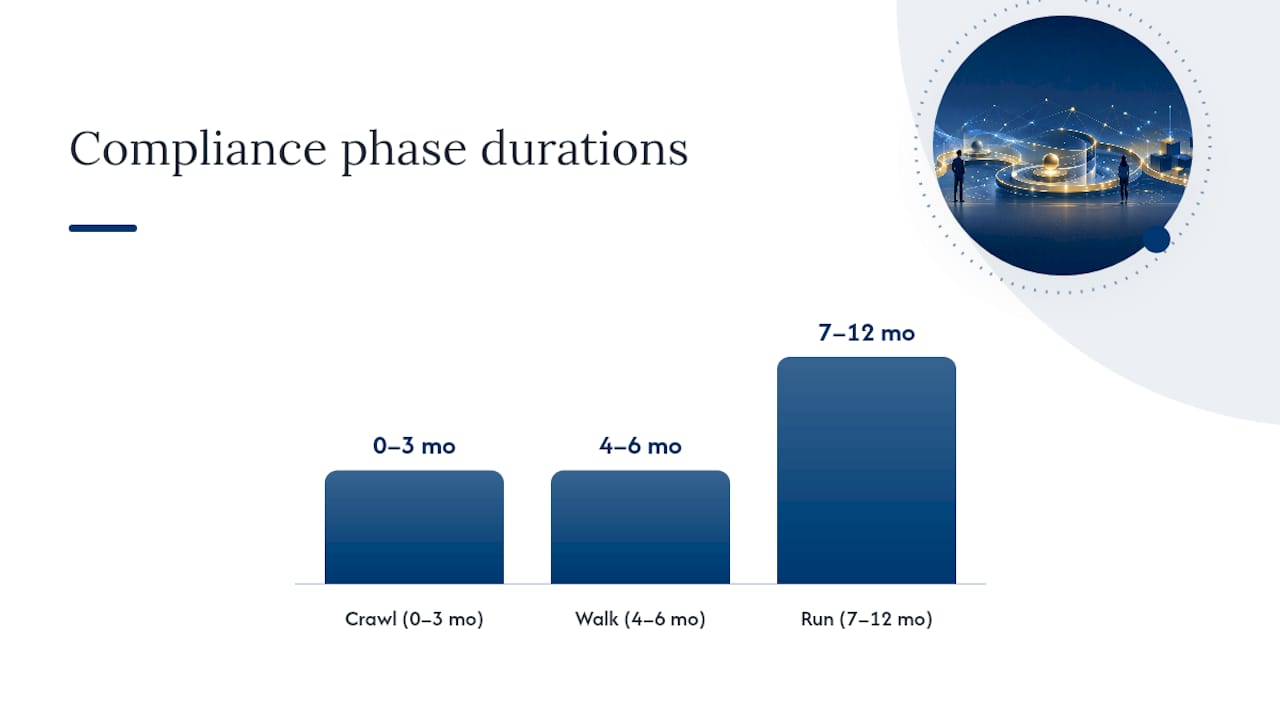
- A Crawl Walk Run Timeline for Startup Compliance
- What Records and Metrics Prove Your Program Actually Ran
- What Counsel Actually Looks for When Preparing an Evidence Pack
- Compliance as a Business Enabler, Not a Cost Center
- How Murphy’s Law Helps You Build an Audit-Ready Compliance Program
- Where to Verify These Rules Directly
- Sources
- FAQ
What Regulatory Perimeter and Obligations Apply to Your Crypto Startup
Before you build a single control, figure out which laws actually reach your business. This is an activity-based test, not a product label. If your platform holds customer funds, converts between fiat and virtual currency, or facilitates transfers on behalf of others, you likely qualify as a money services business (MSB) under FinCEN’s definitions, which triggers registration and a written AML program under the Bank Secrecy Act. A pure software wallet with no custody may fall outside that perimeter. A custodial exchange almost never does.
State money transmitter licensing (MTL) is the next layer, and it gets expensive fast. Most states require a license once you take custody of customer funds or facilitate transmission, and the triage question is simple: does your business ever hold value on behalf of someone else, even briefly? If yes, you need a state-by-state licensing map before you scale marketing spend.
Token issuance raises separate questions entirely. The SEC’s proposed Regulation Crypto Assets includes a Startup Exemption permitting raises up to $5 million over four years and a Fundraising Exemption up to $75 million annually under specified disclosure conditions, according to SEC Chair Atkins’s 2026 statement. Any token, staking product, or yield feature warrants a conversation with securities counsel before launch, not after a subpoena.
Banks and examiners will ask for the same evidence regardless of your business model:
- A written regulatory perimeter memo explaining why you are (or are not) an MSB
- Your FinCEN registration confirmation
- A current AML policy with a named owner
- A one-page risk assessment covering customer, product, and geographic exposure
Core Components of a Crypto Compliance Program
Once you know your perimeter, the actual program comes down to seven interlocking controls. None of them need to be sophisticated on day one. They need to exist, be documented, and scale as your volume grows.
- AML and sanctions risk assessment. Score your risk across five dimensions: customer type, product features, geography, transaction size, and delivery channel. A startup can complete this on one page and update it quarterly.
- Governance. Write a short compliance charter, name an owner with authority to halt onboarding or freeze accounts, and define an escalation path to the founder or board. Grant Thornton’s 2026 guidance is blunt about this: leadership engagement, or “tone from the top,” is now a baseline expectation, not a nice addition.
- KYC/KYB onboarding. Build tiered verification. Low-risk retail users need identity verification and screening. Business accounts need beneficial ownership disclosure. High-risk customers, meaning large volume, high-risk jurisdictions, or unusual fund sources, need enhanced due diligence before you open the account, not after.
- Transaction monitoring and KYT. Blockchain analytics tools flag typologies like structuring, rapid layering through mixers, or exposure to sanctioned wallets. Start with three to five scenarios tied to your actual product flow rather than a generic vendor template.
- Sanctions screening. OFAC expects ongoing screening against its lists, plus documented controls when a match occurs, a standard reinforced in current OFAC virtual currency guidance.
- SAR workflow. When an alert escalates to a suspicious activity report, you generally have 30 days to file. Build a template now: subject information, activity summary, supporting transaction data, and your investigator’s narrative.
- Travel Rule readiness. If you transfer value to other virtual asset service providers above the applicable threshold, you need a plan for exchanging originator and beneficiary information, whether through a vendor network or a built solution. Our Travel Rule guide breaks down vendor tradeoffs in more detail.
Pro Tip: Build your first three monitoring scenarios around the fraud patterns you’re most likely to see, structuring, mixer exposure, and sanctioned-jurisdiction transfers, rather than copying a generic bank template that ignores how your product actually moves money.
A Crawl Walk Run Timeline for Startup Compliance
Founders overbuild or underbuild almost every time, and both mistakes get expensive. A staged model matches your obligations to your actual size, an approach Blockchain Council recommends explicitly for early-stage crypto firms.
Months 0 to 3 (Crawl): Draft the regulatory perimeter memo, complete the one-page risk assessment, appoint your compliance owner, deploy basic KYC and sanctions screening, and stand up three monitoring scenarios.
- Register with FinCEN if your activity qualifies
- Document your AML policy, even in draft form
- Open a compliance file for board reporting
Months 4 to 6 (Walk): Integrate blockchain analytics for KYT, automate sanctions screening rather than running it manually, stand up case management for alerts, formalize your SAR workflow, and train staff on red flags.
Months 7 to 12 (Run): Commission independent testing of your program, assemble evidence packs for banking partners and regulators, pursue state licensing where required, and set a board reporting cadence.
Most seed and Series A startups handle Phase 1 with founder time and outside counsel, then bring in a fractional or full-time compliance officer once transaction volume justifies the headcount. Our guide to the compliance officer role covers when that hire makes sense.
What Records and Metrics Prove Your Program Actually Ran
A policy nobody can point to in an exam is not a program. Regulators and banking partners want documented alert reviews, SAR narratives, and case timelines, not just a binder of procedures, per SphinxHQ’s compliance-building guidance. SAR filings and their supporting documentation should be retained for five years.
Each case file needs the alert trigger, the investigator’s analysis, supporting transaction data, and a documented decision, whether that decision was to close the alert or escalate to a SAR. The metrics below show examiners and bank partners that your program is tuned, not just installed.
| Metric | Why it matters |
|---|---|
| Onboarding approval/rejection rate | Shows your risk tiers are actually filtering applicants |
| Alerts generated per monitoring rule | Flags rules that are too loose or too noisy |
| False positive rate | High rates waste investigator time and signal poor tuning |
| Time-to-close per alert | Slow closure timelines are a common exam finding |
| SAR conversion rate | Tracks what share of escalated alerts become filings |
Tracking these lets you fine-tune monitoring rules without adding headcount every quarter.
What Counsel Actually Looks for When Preparing an Evidence Pack
When Murphy’s Law assembles a compliance record for a bank meeting or a regulatory inquiry, the same items come up every time: the perimeter memo, the current risk assessment, policy documents with revision dates, and a handful of representative case files showing the alert-to-resolution timeline.
A sanctions hit or a major SAR subject demands immediate triage, not a wait-and-see approach. The response sequence matters: freeze the relevant activity, document the decision rationale in real time, and loop in counsel before you file or close.
Typical engagement phases follow a consistent pattern:
- Gap assessment against your current perimeter and controls
- Policy drafting or revision to close identified gaps
- Evidence pack assembly for banking or regulator conversations
- Ongoing regulatory response support as inquiries arise
Founders often assume documentation is a formality. Examiners and banking partners treat it as the entire case.
Compliance as a Business Enabler, Not a Cost Center
The founders who struggle most treated compliance as paperwork to finish before the “real” work of building product. That framing gets it backwards. A banking relationship, a Series A term sheet, and a regulator’s benefit of the doubt all trace back to whether leadership set the tone from the top and gave the compliance owner actual authority to slow down a launch when the risk assessment said to. I have seen a single well-documented risk memo prevent an account freeze that would have taken months to unwind. Treat the function as infrastructure, not overhead.
— Mark
How Murphy’s Law Helps You Build an Audit-Ready Compliance Program
Murphy’s Law is the practical alternative to assembling a compliance program from scattered blog posts and vendor sales decks. We build the actual documents examiners and banks ask for: gap assessments against your specific product model, written AML programs, SAR workflow design, and evidence packs assembled for bank and regulator meetings, not generic templates retrofitted to your business.
A typical engagement moves from gap assessment to policy drafting to evidence pack assembly, giving you audit-ready records, a clearer path to licensing where it applies, and a founder or compliance officer who can walk into a regulator meeting prepared instead of improvising. If your startup is past the idea stage and handling real customer funds, waiting until a bank asks for documentation you don’t have is the expensive way to learn this. Visit our crypto compliance consulting page to schedule a gap assessment and see exactly where your current program stands.
Where to Verify These Rules Directly
- FinCEN for MSB registration and Bank Secrecy Act requirements
- OFAC guidance on virtual currency sanctions obligations
- SEC statements on Regulation Crypto Assets for fundraising exemption details
This article is general information, not a substitute for advice from a qualified lawyer. Consult a qualified legal professional about your own circumstances before acting on anything here.
Sources
- SEC: Statement on Regulation Crypto Assets (Atkins) 2026-08-18
- Grant Thornton: Crypto compliance in 2026
- Blockchain Council: Crypto compliance program for startups
- SphinxHQ: How to build a crypto AML compliance program (U.S.)
FAQ
Is the CLARITY Act Going to Pass?
The bill remains under active congressional negotiation as of 2026, and its digital asset market structure provisions could reshape SEC and CFTC jurisdiction if enacted, but no final passage date is confirmed.
Can the IRS See Your Crypto Wallet?
The IRS can obtain wallet and transaction data through exchange reporting requirements, John Doe summonses, and blockchain analytics tools, so most on-exchange activity is traceable to a taxpayer.
Who Regulates Crypto in America?
No single agency has exclusive jurisdiction. FinCEN oversees AML and MSB registration, the SEC regulates tokens that qualify as securities, the CFTC oversees crypto derivatives and commodity-like tokens, and state regulators handle money transmitter licensing.
Can the FBI Track Crypto?
Yes. The FBI works with blockchain forensic tools and exchange KYC records to trace stolen or laundered funds across wallets, which is also why maintaining your own KYC and transaction records matters if you’re ever a fraud victim seeking recovery through litigation.