
DeFi compliance means aligning a protocol’s design, governance structure, and surrounding services with anti-money laundering, sanctions, and securities rules wherever a person or entity exercises meaningful control. The Financial Action Task Force applies this control test globally, FinCEN applies parallel logic under the Bank Secrecy Act, and the SEC evaluates token arrangements under securities law regardless of what a project calls itself. “Decentralized” branding does not exempt a protocol from any of this.
The verdict: regulators look past labels to function and control. Governance-token concentration, admin keys, upgrade power, and fee flows are treated as evidence that somebody is in charge. Murphy’s Law Crypto builds compliance programs around that reality, not around the hope that decentralization alone provides legal cover.
What to do in the next 90 days:
- Map your protocol’s actual control points (admin keys, multisig signers, fee recipients, upgrade authority).
- Set freeze and stop criteria for sanctioned addresses and high-risk counterparties.
- Integrate baseline know-your-transaction (KYT) screening into your front end and monitoring stack.
- If your team holds any of the levers above, you likely have compliance obligations today, not someday.
- Waiting for “final” regulatory clarity is a losing strategy. Enforcement moves faster than consensus.
Key Takeaways
DeFi compliance succeeds when protocols pair control-based risk mapping with continuous screening, documented governance, and legal review before regulators force the issue.
| Point | Details |
|---|---|
| Control determines obligation | FATF’s test means admin keys, fee flows, and upgrade power can trigger AML duties regardless of “decentralized” branding. |
| Screen continuously, not once | Pre-interaction, time-of-check, and post-execution monitoring together catch risks a single onboarding KYC check misses. |
| Privacy and compliance can coexist | Zero-knowledge attestations and DID let protocols verify status without centrally storing personal data. |
| Governance structure creates liability | Multisig signers, treasury managers, and concentrated token holders all carry potential control exposure. |
| Legal review closes the gap | Murphy’s Law Crypto helps protocols design compliance programs and defend against regulatory action before enforcement escalates. |
Table of Contents
- Why DeFi Regulatory Compliance Actually Matters
- What Does the Regulatory Landscape Look Like for DeFi?
- What AML and KYC Controls Does a DeFi Project Need?
- Which Technical Controls Support DeFi Compliance?
- Who Is Responsible for Compliance in a DAO?
- How Do You Build a DeFi Compliance Program Step by Step?
- How Much Does DeFi Compliance Cost and How Long Does It Take?
- What Are the Most Common DeFi Compliance Mistakes?
- How Murphy’s Law Crypto Supports DeFi Compliance Programs
- Why Do Cross-Border Rules Complicate DeFi Compliance?
- How Do You Balance Privacy With DeFi Compliance Obligations?
- Do Decentralized IDs Change DeFi Compliance Requirements?
- What Legal Risk Do Developers and Node Operators Face?
- How Does Multi-Chain Complexity Affect Compliance Integration?
- DeFi Compliance: A Practitioner’s Take on What Actually Works
- Get Legal Support for Your DeFi Compliance Program
- Sources
- FAQ
Why DeFi Regulatory Compliance Actually Matters
Compliance failures in DeFi carry criminal exposure, not just civil penalties. Operators who control smart contracts, treasuries, or front ends have faced personal liability when their protocols facilitated money laundering or sanctions evasion, and that exposure does not disappear because a DAO voted on the decision.
The downside risks stack up fast:
- Criminal referrals and asset seizures against founders and operators who exercised control.
- OFAC-driven asset freezes and forced delistings from exchanges and aggregators.
- Banking and fiat on/off-ramp cutoffs once a protocol develops an AML reputation problem.
- Shareholder and investor litigation when compliance failures trigger enforcement or losses.
Getting it right unlocks the opposite: institutional liquidity providers increasingly require AML attestations before allocating capital, and banks are far more willing to maintain relationships with protocols that can show documented controls. Recent Treasury enforcement actions have targeted specific wallet addresses and mixing services, and the U.S. Treasury’s press releases make clear that sanctions screening is not optional infrastructure. It is the baseline cost of operating.
What Does the Regulatory Landscape Look Like for DeFi?
No single global rulebook governs decentralized finance, but four reference points define most compliance obligations that actually get enforced.
- FATF’s control test. A DeFi arrangement falls under AML rules wherever a natural or legal person exercises control or sufficient influence, with governance-token concentration and admin privileges as the primary indicators, per the Updated Guidance on VA/VASP.
- FinCEN’s BSA guidance. Virtual-asset activities that function as money transmission trigger AML program obligations, regardless of the technical architecture underneath.
- OFAC’s sanctions posture. Treasury enforcement treats sanctions screening as a strict-liability obligation for anyone with the technical ability to block a transaction.
- SEC securities clarifications. The SEC has continued to clarify how federal securities laws apply to crypto assets, building on enforcement themes it first signaled in 2018.
Whether any of this applies to your protocol depends heavily on facts: who holds keys, who collects fees, who can pause the contract. That “it depends” answer is precisely why founders should get a securities law risk review before launch rather than after a subpoena arrives. Cross-border differences add another layer. What satisfies FATF’s standard in one jurisdiction may not satisfy a stricter domestic implementation elsewhere.
What AML and KYC Controls Does a DeFi Project Need?
Effective AML controls in DeFi combine identity checks, transaction monitoring, and documented escalation, adapted to a permissionless environment where counterparties often never register anywhere.
A practical control stack includes:
- KYC/KYB checks for any interface, wallet-connect flow, or fiat gateway where you have direct counterparty relationships.
- KYT (know-your-transaction) and behavioral screening for wallets interacting with your smart contracts.
- Sanctions and PEP screening against OFAC and equivalent watchlists, refreshed continuously rather than at onboarding only.
- Transaction monitoring tuned to flag structuring, rapid layering, and mixer-linked flows.
- SAR/STR filing processes with clear internal thresholds for escalation.
- Record retention policies that preserve screening decisions and their underlying evidence.
Screening needs to happen at three points: before a user connects a wallet (pre-interaction), at the moment a transaction is submitted (time-of-check, watching the mempool for sanctioned addresses), and continuously afterward through post-execution monitoring. A protocol that screens only once, at onboarding, misses everything that happens after that first handshake.
Pro Tip: Pair privacy-preserving attestations with off-chain identity verification. A user proves they have passed KYC without your protocol storing their passport scan. This satisfies regulator expectations around AML while reducing the data breach liability that comes with hoarding personally identifiable information.
Case management matters as much as detection. If your team cannot produce a clean audit trail showing who reviewed an alert and what they decided, you have not actually built a compliance program, you have built a dashboard. Tools discussed in Murphy’s Law’s KYC program guide for blockchain startups walk through vendor selection for exactly this reason.
Which Technical Controls Support DeFi Compliance?
Technical controls turn policy into enforceable behavior at the protocol level, and this is where most DeFi compliance programs either succeed or quietly fail.
Core tooling categories include:
- On-chain analytics and KYT engines that score wallet risk in real time.
- Sanctions watchlist feeds integrated directly into transaction-screening logic.
- Zero-knowledge proof and decentralized identity (DID) integrations for privacy-preserving verification.
- Mempool and time-of-check monitoring to catch sanctioned addresses before settlement finalizes.
- Oracle design that reliably delivers sanctions-list updates on-chain without introducing a single point of manipulation.
On the smart contract side, OWASP’s Smart Contract Top 10 identifies the vulnerability classes auditors check for, and compliance teams should treat that list as a baseline, not a ceiling. Minimize admin-key privileges, document your upgrade governance process, build explicit compliance hook interfaces into contract architecture, and maintain pausability or escape hatches for genuine emergencies. Every one of these needs audit evidence and test coverage on record, because “we built it securely” is not credible without proof.
Pro Tip: Zero-knowledge attestations let a protocol confirm a wallet cleared sanctions screening without exposing the underlying identity data on-chain. This preserves the audit trail regulators want while avoiding the privacy tradeoffs that centralized KYC databases create.
Who Is Responsible for Compliance in a DAO?
DAO structures do not eliminate legal responsibility, they redistribute it across everyone who exercises meaningful influence over the protocol.
Regulators and litigators generally look at five categories of participants: core developers, multisig or front-end operators, treasury managers controlling fee flows, active governance-token voters, and third-party integrators who route volume through the protocol. Any of these roles can constitute the “control or sufficient influence” that FATF’s guidance uses to bring an arrangement into AML scope.
A defensible governance structure includes clearly documented role definitions, multisig threshold controls with named signers, on-chain and off-chain decision logs, minimized administrative privileges, and a formal upgrade process. Token concentration among a handful of wallets or unilateral admin-key authority are exactly the indicators FATF flags as de facto control, and founders who assume a governance vote insulates them personally are often wrong. Executives facing this exposure should review Murphy’s Law’s breakdown of personal liability risk for crypto executives before, not after, a DAO vote creates a paper trail.
How Do You Build a DeFi Compliance Program Step by Step?
Building a compliance program is sequential work. Skipping steps to reach “done” faster usually produces gaps that surface during an actual investigation.
- Risk assessment. Map control points, jurisdictional exposure, and transaction patterns.
- Policy drafting. Write AML, sanctions, and SAR escalation policies matched to your actual risk profile.
- Technology deployment. Integrate KYT, sanctions screening, and case management tooling.
- Personnel. Assign or hire a compliance officer with clear authority to act on alerts.
- Monitoring. Launch continuous transaction monitoring and periodic model tuning.
- Reporting. Establish SAR/STR filing cadence and regulator communication protocols.
Realistic milestones look like: minimum viable screening within 30 days, documented policies and initial monitoring within 90 days, full case management and audit trails within 180 days, and an annual program review thereafter. Prioritize controls that prevent sanctions exposure first. Regulators consistently treat sanctions violations more harshly than AML gaps, and demonstrating good-faith effort matters even when your program isn’t complete.
Build a simple responsibility matrix: who owns KYT alert triage, who signs off on SAR filings, who schedules smart contract audits, and who updates policy language when guidance changes. Murphy’s Law’s compliance officer guide covers how to structure that role for a DeFi-specific team.
How Much Does DeFi Compliance Cost and How Long Does It Take?
Budget and timeline depend heavily on how many chains you operate on and how broad your user base is geographically, but rough benchmarks hold across most projects.
A minimum viable screening setup (sanctions and basic KYT) typically launches within 30 days. Expanded monitoring with case management and documented escalation usually takes 90 to 180 days. A full institutional-grade program, including audit trails, DID integration, and regular policy review, often runs closer to 365 days for multi-chain protocols.
Primary cost drivers include analytics and KYT subscription fees, engineering time to build compliance hooks into contracts, legal counsel for policy drafting and regulatory strategy, a dedicated compliance officer’s salary, and reserve budget for forensic investigation if an incident occurs. Multi-chain deployments and broad geographic reach both push costs higher, since screening logic and sanctions lists vary by jurisdiction.
What Are the Most Common DeFi Compliance Mistakes?
Most compliance failures trace back to a handful of repeated errors, not novel edge cases.
- Treating the word “decentralized” as legal protection rather than a factual question regulators will investigate.
- Running KYC once at onboarding and never screening again.
- Ignoring mempool-level, time-of-check risk where a sanctioned address slips through before a block finalizes.
- Poor admin-key hygiene, including shared keys, undocumented signers, or no rotation policy.
- Thin documentation that cannot demonstrate a risk-based decision was actually made.
Enforcement history shows liability tends to follow whoever held control and captured profit, not whoever wrote the whitepaper. Continuous monitoring, documented decisions, and periodic legal review close most of these gaps before they become expensive.
How Murphy’s Law Crypto Supports DeFi Compliance Programs
Murphy’s Law Crypto builds compliance programs for protocols that need to move past theory into an operational, defensible structure.
The firm’s work spans several practical services:
- Compliance program design tailored to a protocol’s actual control structure.
- Blockchain forensic investigations when suspicious activity surfaces.
- Litigation and regulatory defense against enforcement actions.
- Smart contract and governance structure review for compliance gaps.
- Incident response when a breach or sanctions violation is discovered.
Liam Murphy, Esq. has litigated against major counterparties in cases involving Celsius, Terraform Labs, and BitMEX, giving the firm direct visibility into how regulators and courts actually evaluate control and liability in crypto disputes, not just how the rules read on paper.
Pro Tip: Build core screening and documentation in-house, but bring in counsel before you finalize governance structure or respond to any regulator inquiry. Founders who wait until after a subpoena often discover their existing policies were never legally reviewed. Murphy’s Law’s crypto compliance consulting team advises on exactly that transition point.
Why Do Cross-Border Rules Complicate DeFi Compliance?
A DeFi protocol accessible from anywhere is, by definition, subject to whatever AML and securities regimes each user’s jurisdiction imposes, and those regimes disagree constantly.
FATF’s control-based standard is a floor, not a ceiling. Individual countries implement it with varying strictness, and some jurisdictions apply securities-style tests to tokens that other regulators would classify as pure utility assets. A protocol that satisfies FinCEN’s money-transmission framework domestically may still face a different classification the moment a European or Asian regulator examines the same fee structure and governance model. The UNODC’s global AML program illustrates just how fragmented international cooperation on illicit finance remains, even among governments actively coordinating.
This creates a genuine operational problem: geofencing does not work cleanly in a permissionless system, and most protocols cannot verify a user’s actual jurisdiction with certainty. Front-end operators sometimes attempt IP-based blocking, but that is trivially circumvented and provides weak legal cover at best.
The practical response is not chasing perfect global compliance. It is documenting a defensible, risk-based approach: screening against the strictest applicable standard for your user base, maintaining records that show you considered jurisdictional exposure, and adjusting as enforcement patterns clarify which regulators are actually active. Protocols operating across many chains and many user bases face compounding versions of this problem, since each additional jurisdiction adds its own screening obligations layered on top of the others.
How Do You Balance Privacy With DeFi Compliance Obligations?
Compliance and privacy pull in genuinely opposite directions in DeFi, and pretending otherwise produces bad architecture decisions.
AML rules generally expect identity verification, transaction history review, and reporting to authorities when suspicious activity appears. Privacy expectations, and in some jurisdictions actual data protection law, push toward minimizing what personal data a protocol collects and stores in the first place. Storing full KYC files on wallets that interact with your contracts creates a honeypot of personally identifiable information, exactly the kind of centralized data store that attracts both hackers and regulatory data protection scrutiny.
Zero-knowledge proofs offer a workable middle path. Louis Federal Reserve](https://research.stlouisfed.org/publications/review/2021/02/05/decentralized-finance-on-blockchain-and-smart-contract-based-financial-markets) on DeFi’s structural differences from traditional finance. The attestation exists on-chain. The passport scan does not.
This doesn’t eliminate every tension. Regulators still expect an auditable trail showing who made screening decisions and why, which means someone, somewhere, holds identity data even in a ZK-based system. The practical question becomes who holds it, for how long, and under what access controls. A third-party attestation provider holding minimal data under a strict retention policy is a materially different risk profile than a protocol’s own smart contract storing raw KYC documents in an accessible database. Teams building compliance architecture need to make that distinction explicit in their own documentation, not leave it implied.
Do Decentralized IDs Change DeFi Compliance Requirements?
Decentralized identity (DID) systems let a user carry a verified credential across multiple protocols instead of repeating KYC every time they connect a wallet somewhere new.
The compliance value is real: a user completes identity verification once with a trusted issuer, receives a cryptographic credential, and then presents that credential to any protocol requiring proof of KYC status. The protocol never touches the underlying documents. It simply verifies the credential’s validity, similar in spirit to how ZK attestations function but built around portable, reusable identity rather than one-off proofs.
DIDs don’t resolve every compliance question on their own, though. A credential is only as trustworthy as its issuer, so protocols relying on DID need to vet which issuers they’ll accept and document that vetting decision. Regulators evaluating a protocol’s AML program will want to see that the DID framework in use actually meets equivalent standards to traditional KYC, not just that it uses impressive cryptography. There’s also an interoperability problem: DID standards are still fragmenting across different chains and identity networks, which means a credential trusted on one protocol may not be recognized on another.
For compliance teams, the practical takeaway is that DID adoption reduces user friction and reduces the amount of raw PII any single protocol stores, but it shifts due diligence upstream to issuer vetting rather than eliminating due diligence altogether. Treat DID integration as a component of your identity verification stack, not a replacement for a documented compliance policy.
What Legal Risk Do Developers and Node Operators Face?
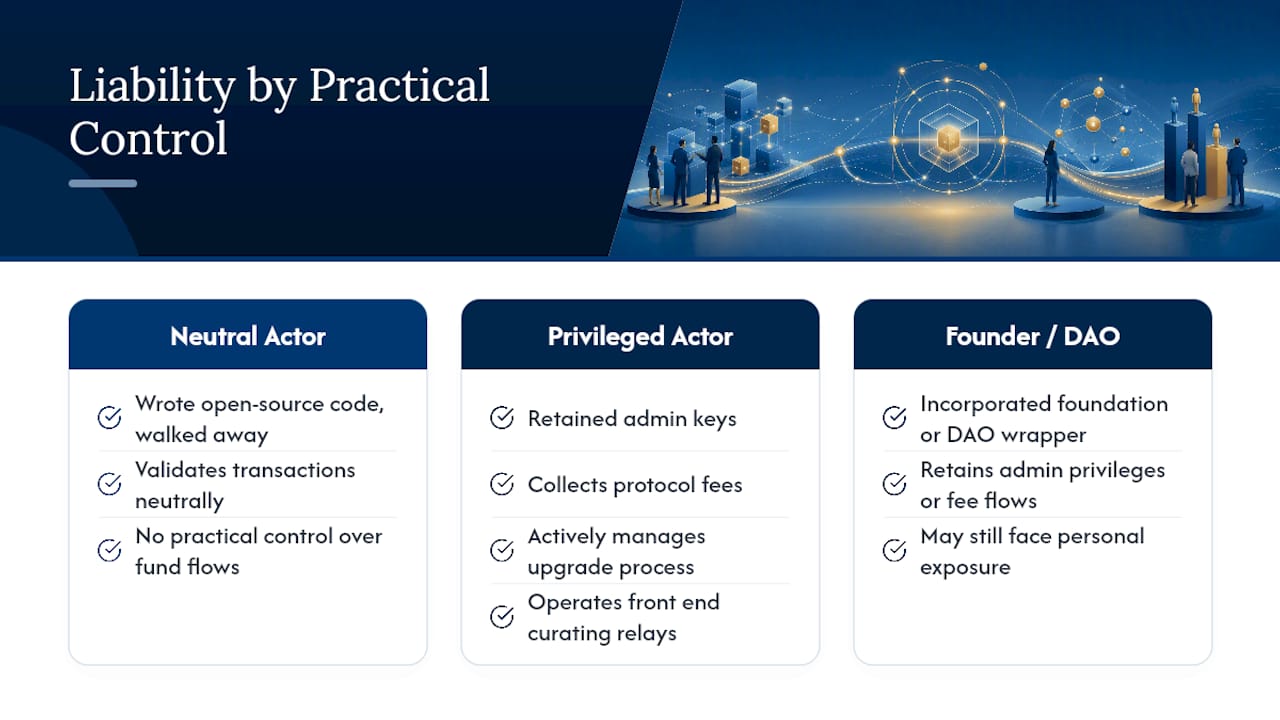
Writing code or running infrastructure does not automatically create liability, but it stops being neutral the moment that code or infrastructure gives someone effective control over fund flows.
Courts and regulators increasingly ask a functional question: did this person or entity have the practical ability to prevent, alter, or profit from the transaction in question? A developer who wrote open-source code and walked away faces a different risk profile than one who retained admin keys, collects protocol fees, or actively manages an upgrade process. Node operators face a parallel question. Simply validating transactions under a neutral protocol is different from operating a front end that curates which transactions get relayed, or from running infrastructure that could technically block sanctioned addresses but chooses not to.
The ACAMS analysis of DeFi compliance captures the industry-standard supervisory thinking here: regulators care about the function performed, not the label attached to it. Custody, exchange, and transfer functions carry obligations regardless of whether a human or a smart contract executes them.
This matters most for founders who assume incorporating a foundation or DAO wrapper insulates them personally. It often does not, particularly when enforcement actions target individuals who retained practical control after formally “decentralizing.” Anyone holding admin privileges, fee flows, or upgrade authority should assume personal exposure is possible and structure governance accordingly, ideally with the kind of liability review covered in Murphy’s Law’s guide to crypto executive personal liability.
How Does Multi-Chain Complexity Affect Compliance Integration?
Every additional chain a protocol deploys on multiplies the compliance surface area, because sanctions lists, transaction monitoring, and identity standards do not automatically synchronize across chains.
A protocol operating on multiple networks needs KYT screening tuned separately for each chain’s transaction patterns, since wallet clustering heuristics that work well on one network can produce false positives or blind spots on another. Bridges introduce their own risk layer entirely. Funds crossing from one chain to another can obscure the transaction history that KYT tools rely on, effectively laundering the audit trail even when neither chain individually has a compliance gap. Oracle-fed sanctions data needs to reach every chain your protocol touches, with consistent update timing, or you end up screening against a stale list on one network while your primary chain runs current data.
Cross-chain governance adds another wrinkle. If a DAO controls contracts deployed on five different networks through a single multisig, that multisig’s signers carry control exposure across all five, not just wherever the DAO happens to be formally registered. Compliance teams building for multi-chain environments should treat each chain’s deployment as requiring its own risk assessment, then unify the results into a single case management system so an analyst reviewing an alert has full visibility across every chain a suspicious wallet has touched, not just the one where the alert fired.
DeFi Compliance: A Practitioner’s Take on What Actually Works
The conventional advice tells founders to “wait for regulatory clarity” before building compliance infrastructure. That advice is backwards, and the enforcement record proves it. Regulators have never needed a finished rulebook to bring a case. FATF’s control test and FinCEN’s function-based approach already give them everything necessary to act, and they have acted, repeatedly, against protocols that assumed decentralization was a legal shield rather than a factual claim someone would eventually test in court.
What gets underestimated is how much documentation matters relative to perfection. A protocol with a genuinely risk-based, imperfect compliance program that shows its reasoning tends to fare far better in an investigation than one with no program at all, even if neither caught every bad actor. Regulators reward evidence of good faith. They punish willful blindness.
The priority order that actually protects a project isn’t “build the fanciest KYT stack.” It’s map your control points honestly, document every governance decision, and get legal eyes on your structure before a subpoena forces the question. Technology without that legal framing is theater.
Get Legal Support for Your DeFi Compliance Program
Building a defensible DeFi compliance program from scratch, or defending one that’s already drawn regulatory attention, is not a project most in-house teams should tackle alone. Murphy’s Law Crypto is the option for protocols and founders who need actual litigation experience behind their compliance strategy, not just a vendor selling screening software. Liam Murphy, Esq. has litigated against counterparties in some of the industry’s highest-profile cases, including Celsius, Terraform Labs, and BitMEX, which means the firm’s compliance advice is shaped by watching how regulators actually build cases, not just how guidance documents read.
Whether you’re designing a compliance program from the ground up or responding to an active regulatory inquiry, Murphy’s Law’s crypto compliance consulting team can review your governance structure, screening controls, and documentation before a regulator does it for you. Start with a consultation to map where your protocol’s actual exposure sits.
This article is general information, not a substitute for advice from a qualified lawyer. Consult a qualified legal professional about your own circumstances before acting on anything here.
Sources
- Updated Guidance on VA/VASP (FATF)
- FinCEN guidance on convertible virtual currencies
- SEC press release (2026) — clarifies application of federal securities laws to crypto assets
- U.S. Treasury press release
- OWASP smart contract top 10
FAQ
Is DeFi Illegal in the US?
DeFi itself is not illegal in the United States, but specific activities within a protocol, such as unregistered securities offerings or unlicensed money transmission, can trigger legal exposure depending on who controls the protocol and how it functions. Whether a given arrangement crosses that line depends on facts specific to each protocol, which is why founders should consult counsel rather than rely on general assumptions.
What Does DeFi Stand For?
DeFi stands for decentralized finance, a term for financial services, such as lending, trading, and asset management, built on blockchain networks and executed through smart contracts rather than traditional intermediaries.
How Risky Is DeFi From a Compliance Standpoint?
DeFi carries elevated compliance risk because pseudonymity, cross-border access, and smart contract automation make sanctions evasion and money laundering harder to detect than in traditional finance. Protocols that skip continuous screening and documented governance face real enforcement exposure, as Treasury and SEC actions have repeatedly shown.
Is Bitcoin Considered DeFi?
Bitcoin itself is not typically classified as DeFi since it functions primarily as a decentralized store of value and payment network rather than a platform for lending, trading, or other automated financial services. DeFi generally refers to smart contract based applications, often built on networks like Ethereum, that replicate financial services without centralized intermediaries.
Who Is Legally Responsible for a DeFi Protocol’s Compliance?
Legal responsibility generally follows control, meaning developers, multisig signers, treasury managers, and governance participants who exercise meaningful influence over a protocol can all face liability. Murphy’s Law Crypto helps founders and operators assess exactly where that exposure sits before regulators make the determination for them.