
A token is not launch-ready until every item on this compliance checklist is documented, reviewed by qualified legal counsel, and signed off by the appropriate owner. The single highest-priority requirement is compliance by design, building legal and operational controls into the token’s architecture before a single line of code is finalized, not after the first exchange conversation. According to industry guidance, a modern compliant token launch typically requires months of preparation and a realistic budget that often falls within a moderate range depending on target exchanges and jurisdictional complexity. If your team is less than six months from a planned token generation event (TGE) and any of the items below remain unresolved, pause launch activity and engage counsel immediately.
Pre-launch must-do checklist (launch-blocking items):
- Entity formed in a legally defensible jurisdiction with governance documents executed
- Token classification analysis completed and attorney-reviewed legal opinion in hand
- KYC/AML program documented, vendor contracted, and operational
- Smart contract audit completed with remediation log and auditor attestation
- Custody arrangements confirmed with a qualified custodian
- Vesting and lockup schedules enforced on-chain or via custodial controls
- Whitepaper and risk disclosures reviewed by counsel and version-controlled
- Listing readiness package assembled (legal opinion, audit report, KYC/AML evidence, team KYC)
- Tax and accounting setup complete with a crypto-savvy accountant engaged
- Sanctions screening active and documented
Concrete next steps by timeline:
- Immediate (pause if missing): Legal opinion, KYC/AML vendor, smart contract audit engagement, entity formation
- 3–6 months out: Custodian outreach, listing prep, vesting enforcement, tax setup
- 6–12 months out: Ongoing monitoring program, incident response playbook, exchange relationship management
Pro Tip: If a Tier-1 exchange or institutional custodian asked for your compliance data room today, could you produce it within 48 hours? If the answer is no, that gap is your launch risk.
Key Takeaways
A compliant token launch requires completing every launch-blocking item before TGE, with legal opinion, KYC/AML program, smart contract audit, and custody arrangements as the four items that no exchange or institutional partner will waive.
| Point | Details |
|---|---|
| Preparation timeline | Industry guidance estimates several months and a variable budget range for a fully compliant launch targeting institutional-grade exchanges. |
| Token classification | A written Howey analysis and attorney-reviewed legal opinion are required before finalizing token design or marketing. |
| KYC/AML program | FinCEN and FATF baseline requirements apply at every touchpoint involving fiat, custody, or identifiable purchasers. |
| Custodian lead time | Custodian build-out takes roughly 3–9+ months; outreach must begin well before TGE, not after exchange conversations start. |
| Audit and remediation | All critical and high smart contract findings must be remediated and attested by the auditing firm before any listing package is submitted. |
| Murphyslawcrypto | The firm provides legal opinions, KYC/AML program build-out, audit-ready documentation review, and regulatory defense for token launch teams. |
Table of Contents
- What entity structure and governance documents do you need before token design finishes?
- How do you classify your token and reduce securities-law exposure?
- What disclosures and documentation do exchanges and regulators expect?
- How do you build a KYC/AML program that meets partner and regulator expectations?
- What licensing risks do state money-transmitter laws and broker/dealer rules create?
- What do smart contract audits and remediation logs need to cover?
- How do private rounds, SAFTs, vesting, and lockups affect your legal obligations?
- What do exchanges and custodians require before listing or custody onboarding?
- What tax and accounting setup do you need before a token event?
- What ongoing compliance does your token need after TGE?
- Consolidated pre-launch timeline and sign-off matrix
- What enforcement cases reveal about common token launch mistakes
- Compliance is a product feature, not a pre-launch task
- Murphyslawcrypto’s compliance consulting and legal opinion services
- Sources
- FAQ
What entity structure and governance documents do you need before token design finishes?
Entity selection is not a formality. The jurisdiction where you incorporate, the governance documents you execute, and how you separate founder roles will determine which exchanges will list your token, which banks will open accounts, and how regulators will characterize your control over the protocol.
Entity and jurisdiction considerations:
- Delaware C-Corps remain a common starting point for U.S.-facing projects; the Delaware Division of Corporations provides formation timelines and required filings. Cayman Islands foundations, BVI companies, and Swiss associations each carry different tax, governance, and regulatory profiles.
- Offshore entities do not eliminate U.S. regulatory exposure if founders, investors, or users are U.S. persons. Structure must follow substance.
- Foundation/DAO hybrid structures require documented governance charters that clearly separate protocol governance from commercial operations.
Founder and IP documents to execute before token design:
- Founder vesting agreements with cliff and acceleration terms
- Role separation documentation (who controls treasury, who controls protocol admin keys)
- IP assignment agreements transferring all pre-company work product to the entity
- Founder warranty letters confirming no undisclosed liabilities or competing obligations
- Cap table snapshot signed off by all equity holders
Banking and fiat rails:
Banks conducting KYC on crypto entities will request entity formation documents, beneficial ownership registers, AML policies, and descriptions of the token’s purpose. A clean entity structure with documented governance materially speeds that process. Projects that cannot explain their token’s function in plain language to a compliance officer typically fail banking KYC.
Operational artifacts:
- Board minutes authorizing the token issuance and any private sale
- Vendor contracts with security attestation requirements
- Trademark filings for brand and token marks; USPTO filing fees and steps apply and should be budgeted early
| Formation step | Typical lead time | Owner |
|---|---|---|
| Entity incorporation (Delaware) | 1–2 weeks (expedited) | Founder / outside counsel |
| Governance documents executed | 2–4 weeks | Legal counsel |
| IP assignment completed | 1–2 weeks | Founders + counsel |
| Banking KYC package submitted | 4 weeks | CFO / legal |
| Trademark application filed | 1–2 weeks to file; months to register | IP counsel |
Pro Tip: Execute IP assignment agreements before any token design work begins. Disputes over who owns the protocol’s core IP are among the most expensive pre-launch problems to fix, and they can block a listing entirely.
How do you classify your token and reduce securities-law exposure?
The Howey test, as applied by the SEC and courts, asks whether a transaction involves an investment of money in a common enterprise with an expectation of profits derived from the efforts of others. Most token launches fail at least one prong of that test at some stage of their lifecycle. The question is not whether your token is theoretically a utility token; it is whether the totality of your design, marketing, and distribution creates a reasonable expectation of profit in the mind of a purchaser.
Design signals that push a token toward security status:
- Profit-expectation language in the whitepaper, pitch decks, or social media (“token price will increase as adoption grows”)
- Revenue-sharing mechanics or buyback programs funded by protocol revenue
- Early-insider concentration where a small group controls a majority of supply at launch
- Governance rights that are meaningfully tied to economic returns rather than protocol decisions
- Admin keys or “god-mode” controls that allow the founding team to alter token economics post-launch
Inconsistent admin privilege claims are a particular liability. As Gabriel Shapiro has documented, smart contract controls and decentralization claims must be consistent with public communications; undisclosed admin keys create legal liabilities that are difficult to reverse after issuance.
Token-design controls that reduce securities risk:
- Utility-first design: token access to a live, functional product at or before TGE
- Independent demand drivers that are not contingent on the founding team’s ongoing efforts
- Transparent, on-chain vesting and lockup schedules for all insider allocations
- No buyback or revenue-distribution mechanics in the initial protocol design
- Governance rights that are genuinely decentralized and do not confer economic entitlements
Key regulatory standard: The SEC’s Investment Advisers Act rule release IA-5653 and related staff guidance are primary references that exchanges and institutional advisers use when evaluating whether a token’s distribution and custody arrangements meet disclosure and registration expectations. A formal legal opinion addressing these standards is not optional for any project seeking Tier-1 exchange listings.
Legal citation checklist:
- Obtain a written Howey analysis from qualified securities counsel before finalizing token design
- Confirm whether any exemption under 17 CFR § 4.13 or Regulation D/S applies to your private sale
- Document the basis for any “utility token” conclusion in a memo that can be produced in diligence
- Review SEC crypto regulations and CFTC jurisdictional considerations for commodity-law exposure
Pro Tip: Audit every piece of marketing copy, every Discord announcement, and every investor presentation for profit-expectation language before launch. A single tweet promising “token holders will benefit from protocol revenue” can undermine an otherwise defensible utility-token analysis.
What disclosures and documentation do exchanges and regulators expect?
Exchanges, institutional partners, and regulators will look for two distinct document types: a technical whitepaper describing the protocol’s architecture and a regulatory disclosure document addressing token economics, risk factors, and jurisdictional restrictions. Conflating these into a single marketing document is one of the most common and consequential documentation mistakes.
Disclosure bullets that must appear in your regulatory whitepaper:
- Total token supply, circulating supply at TGE, and maximum supply with issuance schedule
- Vesting and lockup schedules for all insider, team, and investor allocations, with on-chain enforcement details
- Description of any admin controls, upgrade mechanisms, or multisig arrangements that affect token economics
- Risk factors: smart contract risk, regulatory risk, liquidity risk, key-person risk, and market risk
- Jurisdictional restrictions: explicit list of excluded jurisdictions and the legal basis for exclusion
- Use of proceeds from any token sale, with allocation percentages
Version control and document storage:
- Maintain a version-controlled document repository (Git-based or equivalent) with timestamped commits for every material change to the whitepaper, terms of service, and privacy policy
- Retain prior versions permanently; regulators and litigants will request version histories
- Store signed legal opinions, audit reports, and KYC/AML attestations in a dedicated due-diligence data room with access logs
Marketing review rules:
Language that creates legal risk includes: projected returns, comparisons to past token performance, statements that the team will “drive” token value, and any implication that purchasers will profit from the team’s efforts. Every piece of external-facing content should pass a legal review before publication.
Pro Tip: Influencer and affiliate promotions must include clear paid-promotion disclosures under FTC guidelines, and the scripts themselves should be reviewed by counsel. An influencer’s undisclosed paid promotion of your token is your legal problem, not just theirs.
How do you build a KYC/AML program that meets partner and regulator expectations?
KYC and AML controls are required at every touchpoint where your project accepts fiat currency, interfaces with a custodial relationship, or sells tokens to identifiable purchasers. FinCEN guidance explains when AML obligations and money-services-business (MSB) rules apply to crypto business models, including transaction monitoring and suspicious-activity reporting requirements. FATF guidance establishes the global baseline that institutional counterparties enforce regardless of the token’s home jurisdiction.
Touchpoints that require KYC/AML at or before TGE:
- All token sale purchasers (private and public rounds)
- Fiat on/off-ramp relationships
- Custodial wallet relationships
- Exchange listing onboarding (team KYC is standard)
Stepwise KYC flow:
- Onboarding: Collect government-issued ID, proof of address, and beneficial ownership information for entities. Use a vendor with liveness detection and document verification.
- Risk scoring: Assign each purchaser a risk tier (standard, elevated, high) based on jurisdiction, transaction size, and PEP/sanctions status.
- Enhanced due diligence (EDD): For high-risk purchasers, collect source-of-funds documentation and conduct adverse-media screening.
- Transaction monitoring: Flag unusual transaction patterns post-TGE using automated monitoring tools calibrated to your token’s expected transaction profile.
- Suspicious activity reporting: Establish a documented escalation path and, where required, file Suspicious Activity Reports (SARs) with FinCEN.
Vendor selection checklist:
- Proof of capability: request sample audit logs and a description of the vendor’s sanctions-list update frequency
- Sanctions list coverage: OFAC SDN list, UN consolidated list, EU consolidated list, and HM Treasury list at minimum
- Travel Rule support: confirm the vendor supports FATF Travel Rule data transmission for transfers above applicable thresholds
- Data retention: confirm the vendor retains records for at least five years and can produce them on regulatory request
- Privacy interplay: confirm the vendor’s data processing agreements comply with applicable privacy laws (GDPR, CCPA) for your user base
Regulatory baseline: FATF’s guidance on virtual assets makes KYC/AML and sanctions screening baseline expectations across member jurisdictions, even where token classification differs. Projects that cannot produce documented KYC/AML programs and vendor attestations will not pass institutional counterparty due diligence, regardless of the token’s legal characterization.
Implementation notes:
- Retain KYC records for a minimum of five years from the date of the transaction
- Document the legal basis for any jurisdiction-based exclusion from KYC requirements
- Require custodian attestations confirming their own AML program meets applicable standards
- Review KYC compliance program guidance for vendor and workflow specifics relevant to blockchain startups
What licensing risks do state money-transmitter laws and broker/dealer rules create?
State money-transmitter license (MTL) requirements are among the most commonly underestimated compliance risks for token projects. Activities that most frequently trigger MTL or broker/dealer exposure include: accepting fiat currency in exchange for tokens, operating a custodial wallet, facilitating peer-to-peer transfers for value, and providing exchange or conversion services. Triggering these requirements without a license creates criminal and civil liability that cannot be retroactively cured.
Activities that commonly trigger licensing requirements:
- Fiat on/off-ramp operations (accepting USD for tokens or converting tokens to USD)
- Custodial services where the project holds private keys on behalf of users
- Transfer-for-value services where the project moves funds between wallets
- Broker or dealer activities in connection with token sales that may be securities
Structural mitigations:
- Use a licensed third-party custodian rather than holding user funds directly
- Geofence token sales to exclude jurisdictions where licensing is required and the project has not obtained a license
- Limit the project’s service scope to avoid triggering the “transfer for value” definition in state MTL statutes
- Engage a licensed money-services business as the fiat on/off-ramp rather than operating that function internally
Estimated timelines and costs for common licensing paths:
| License type | Typical timeline | Estimated cost range | Key risk if absent |
|---|---|---|---|
| State MTL (single state) | 6–18 months | $25,000 | Criminal liability, cease-and-desist |
| FinCEN MSB registration | 180 days from triggering activity | Minimal filing fee | Federal AML enforcement |
| Broker-dealer registration | 12 months | $100,000 | SEC enforcement, disgorgement |
| Custody license (state) | 12 months | $50,000 | Banking partner rejection |
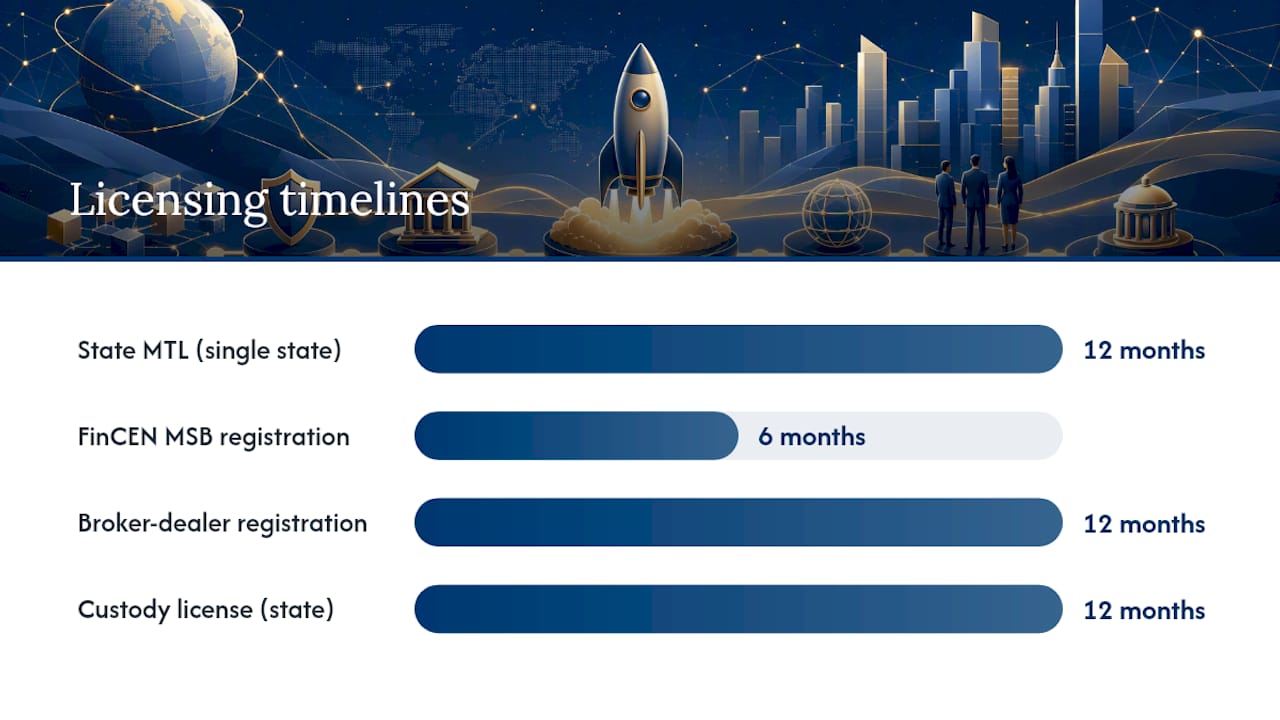
Red flags that will delay listings or banking: unresolved MTL exposure in major U.S. states, undisclosed custodial arrangements, and any history of operating without required licenses. Banking partners and Tier-1 exchanges conduct licensing diligence as a standard step.
Pro Tip: Document your reliance on third-party custodians in writing, including the custodian’s license numbers and the scope of services they provide. That documentation is what you produce when a banking partner or exchange asks how you handle user funds. Verbal assurances do not survive due diligence.
For a detailed breakdown of how crypto fraud laws differ across jurisdictions, including Switzerland, Singapore, UAE, and the U.S., that resource provides a useful comparative framework for jurisdiction selection.
What do smart contract audits and remediation logs need to cover?
Audits and remediation logs are non-negotiable for exchange listing and institutional custody. No Tier-1 exchange will list a token, and no qualified custodian will onboard it, without a completed audit from a recognized firm and a documented remediation log showing how every identified vulnerability was addressed. The audit is not a checkbox; it is the primary technical evidence that your token’s on-chain behavior matches your public claims.
Audit scope checklist:
- Token contract logic (minting, burning, transfer restrictions, admin controls)
- Vesting and lockup contracts
- Treasury and multisig contracts
- Bridge contracts (if applicable)
- Staking and rewards contracts
- Governance contracts and timelock mechanisms
Remediation and attestation requirements:
- Every finding must be categorized by severity (critical, high, medium, low, informational)
- Critical and high findings must be remediated before TGE; medium findings require a documented remediation plan
- Remediation must be verified by the auditing firm in a re-audit or attestation letter
- The final audit report and remediation log must be included in the exchange listing package
Operational security requirements:
- Multisig or MPC key management for all treasury and admin functions, with documented key-holder policies
- Incident response playbook covering smart contract exploits, key compromise, and bridge attacks
- Real-time monitoring dashboards with alerting for anomalous on-chain activity
- Key custody documentation confirming no single point of failure
Pro Tip: Sequence your audits so the final re-audit attestation is complete at least 30 days before your planned TGE. Exchanges require time to review audit artifacts, and a last-minute audit finding that requires remediation will delay your listing by weeks, not days.
How do private rounds, SAFTs, vesting, and lockups affect your legal obligations?
The choice between private and public distribution is not a marketing decision; it changes your registration and investor-qualification obligations under federal securities law. Private allocations to accredited investors under Regulation D require documented accreditation verification. Public sales that reach U.S. persons without a valid exemption create registration exposure that cannot be undone after the fact.
Private allocation and public sale controls:
- Whitelist all private-round purchasers and document their accredited-investor status before accepting funds
- Geofence public sales to exclude U.S. persons unless a valid exemption (Regulation S, Regulation D) is documented
- Confirm that SAFT (Simple Agreement for Future Tokens) structures are reviewed by securities counsel; SAFTs do not automatically confer a securities-law exemption
- Document the basis for any Regulation S exclusion, including IP address verification, residency attestations, and purchase agreement representations
Vesting and lockup mechanics:
- Minimum recommended lockup for team and insider allocations: 12 months cliff, 36–48 months total vesting
- Enforce lockups on-chain where possible; custodial enforcement requires documented custodian instructions and confirmation
- Investor lockups should be reflected in both the purchase agreement and the on-chain token contract
- Any deviation from disclosed lockup schedules after TGE creates both legal and reputational risk
Structural caution: Once tokens are distributed to a large number of holders, correcting a flawed vesting structure or an undisclosed admin control requires either a protocol upgrade (which may itself trigger regulatory scrutiny) or litigation. The cost of fixing a distribution structure post-launch is orders of magnitude higher than designing it correctly before issuance. This is the “one-way door” problem that makes pre-launch legal review non-negotiable.
Contract items to review before signing:
- Purchase agreement representations and warranties (accreditation, residency, no re-sale restrictions violated)
- Grant document terms for advisor and contributor allocations (vesting, clawback, tax treatment)
- SAFT conversion mechanics and the conditions under which tokens are delivered
- Anti-dilution and most-favored-nation clauses in early-round agreements
Pro Tip: Disclose all insider allocations, including advisor grants and ecosystem fund reserves, in the whitepaper and on-chain at TGE. Undisclosed insider supply that hits the market post-launch is one of the fastest ways to trigger both regulatory scrutiny and community backlash simultaneously.
What do exchanges and custodians require before listing or custody onboarding?
Exchanges and institutional custodians will not list or onboard a token based on a whitepaper and a pitch. They require a documented compliance data room, custody readiness evidence, and distribution provenance before any listing conversation advances to a term sheet. According to a16z’s operational guidelines, custodian build-out can take roughly 3–9+ months depending on token complexity and staking or governance requirements, which means custodian outreach must begin well before TGE.
Practical custody checklist:
- Executed custodial services agreement with a qualified custodian
- Custodian confirmation of staking support (if applicable) and governance participation mechanics
- Multisig/MPC proof: documentation of key management architecture and key-holder policies
- Custodian due-diligence artifacts: the custodian’s own audit reports, licensing documentation, and AML attestations
Distribution controls and on-chain provenance:
- Conduct test transactions before the main distribution event to verify wallet addresses and contract behavior
- Generate merkle proofs or equivalent on-chain provenance records for all allocation tranches
- Document tranche logic: which wallets receive which allocations, under what vesting schedule, and with what on-chain enforcement
- Verify all recipient wallet addresses through a documented wallet-verification process before distribution
Listing readiness package:
- Attorney-reviewed legal opinion addressing token classification and applicable exemptions
- Completed smart contract audit report and remediation log
- KYC/AML program documentation and vendor attestations
- Team KYC: all founders and key personnel must complete KYC with the exchange’s compliance team
- Tokenomics documentation: supply schedule, vesting, lockups, treasury management policy
Pro Tip: Contact your target custodian at least six months before TGE, and your target exchanges at least three months before. Both will have their own onboarding timelines, and neither will accelerate them for a project that arrives late. Understand what crypto custody regulation means before those conversations begin.
What tax and accounting setup do you need before a token event?
Tax treatment for token issuances, sales, and distributions must be determined before the first token moves, not after. The IRS treats digital assets as property, which means every issuance event, sale, exchange, and distribution is potentially a taxable event that must be recorded at fair market value on the date of the transaction. Retroactively reconstructing these records is expensive and often incomplete.
Tax and accounting checklist:
- Engage a crypto-savvy accountant or tax attorney before TGE to determine the tax treatment of the token issuance
- Set up accounting software capable of tracking token transactions at the lot level (acquisition date, cost basis, fair market value at disposition)
- Record every issuance event: date, quantity, fair market value, recipient, and the legal basis for the transaction
- Determine revenue recognition treatment for token sale proceeds under applicable accounting standards
- Set up payroll and contractor reporting for any compensation paid in tokens (W-2 or 1099 treatment depending on the arrangement)
- Track capital events: treasury token sales, buybacks, and any protocol-level token burns
Forms and registrations to consider:
- Review IRS Form 15620 and related digital-asset guidance for applicable reporting requirements
- Confirm whether the entity has foreign bank account reporting obligations (FBAR, Form 8938) for offshore treasury accounts
- Register for applicable state tax accounts in jurisdictions where the entity has nexus
Questions to take to your accountant:
- What is the tax treatment of tokens issued to founders and employees (ordinary income vs. capital gain)?
- How should token sale proceeds be recognized if tokens are subject to vesting or lockup?
- What documentation does the IRS expect for a token issuance event?
- Are there transfer-pricing implications for intercompany token transfers between related entities?
Pro Tip: Document the fair market value of every token allocation at the time of grant, including advisor and contributor grants. The IRS will look at the value on the date of issuance, not the date of vesting, for certain grant structures. Getting this wrong creates tax liabilities that compound over time.
What ongoing compliance does your token need after TGE?
Ongoing transaction monitoring, sanctions screening, and robust recordkeeping are required to maintain exchange listings and partner integrations after TGE. Exchanges and custodians conduct periodic compliance reviews, and a project that cannot produce current monitoring logs, updated KYC records, and incident reports will face delisting risk. Legislative activity, such as H.R.3633 in the 119th Congress, demonstrates that token-related rules remain in flux, making continuous monitoring of regulatory developments a compliance requirement in its own right.
Monitoring and recordkeeping checklist:
- Transaction monitoring: run automated monitoring on all on-chain activity associated with the project’s wallets and contracts
- Sanctions screening: screen all new counterparties and re-screen existing ones on a periodic basis (at minimum quarterly)
- KYC record retention: retain all KYC documentation for at least five years from the date of the relevant transaction
- Audit trail: maintain complete logs of all compliance decisions, escalations, and vendor interactions
- Vendor logs: require your KYC/AML vendor to produce periodic audit logs confirming system uptime and screening accuracy
Incident response and reporting workflow:
- Detect: automated monitoring flags an anomalous transaction or a security incident
- Assess: compliance officer reviews the flag and determines whether it meets the threshold for escalation
- Escalate: legal counsel is notified; if a SAR filing is required, it is prepared and submitted within the required timeframe
- Document: the full incident timeline, assessment, and resolution are documented and retained
- Report: if the incident involves a smart contract exploit or material security breach, notify affected exchanges and custodians per contractual obligations
- Review: conduct a post-incident review and update the incident response playbook
Maintaining continuing compliance evidence:
- Produce a quarterly compliance summary for exchange partners that includes monitoring statistics, incident reports, and KYC/AML program updates
- Update the legal opinion annually or whenever there is a material change in the token’s design, distribution, or regulatory environment
- Maintain a regulatory change log documenting how the project has responded to new guidance or legislation
Consolidated pre-launch timeline and sign-off matrix
The table below maps the core compliance workstreams to time buckets leading into TGE, with the owner and sign-off evidence required for each.
| Time bucket | Workstream | Owner | Sign-off evidence required |
|---|---|---|---|
| 90–180 days | Entity formation and governance documents | Founder + outside counsel | Executed incorporation documents, board minutes |
| 90–180 days | Token classification analysis and legal opinion | Securities counsel | Written legal opinion letter |
| 90–180 days | Custodian outreach and onboarding initiation | CFO + legal | Custodian engagement letter |
| 90–180 days | Smart contract audit engagement | CTO + audit firm | Signed audit engagement agreement |
| 60–90 days | KYC/AML vendor contracted and operational | Compliance officer | Vendor contract, test run logs |
| 60–90 days | Whitepaper and disclosure documents finalized | Legal + marketing | Counsel-reviewed, version-controlled documents |
| 60–90 days | Tax and accounting setup complete | CFO + accountant | Accountant engagement letter, accounting system configured |
| 30–60 days | Smart contract audit completed and remediated | CTO + audit firm | Final audit report and remediation log |
| 30–60 days | Listing readiness package assembled | Legal + compliance | Complete data room with all required artifacts |
| 30–60 days | Exchange outreach initiated | CEO + legal | Exchange NDA and initial diligence submission |
| up to 30 days | Custodian integration tested | CTO + custodian | Test transaction receipts, custodian confirmation |
| up to 30 days | On-chain distribution provenance documented | CTO | Merkle proofs or equivalent on-chain records |
| launch day | Go/no-go gate review | All owners | Signed go/no-go checklist with all artifacts confirmed |
Go/no-go gate criteria:
- Legal opinion in hand and reviewed by all founders
- Smart contract audit complete with all critical and high findings remediated and attested
- KYC/AML program operational and vendor attestation received
- Custodian integration confirmed and tested
- Listing readiness package submitted to at least one target exchange
- Tax and accounting setup complete
If a gate fails within 30 days of TGE:
- Immediately notify all exchange and custodian counterparties of the delay
- Do not proceed with token distribution until the failed gate is resolved
- Engage counsel to assess whether the failure creates any disclosure obligation to existing investors
- Document the delay, the cause, and the remediation steps taken
What enforcement cases reveal about common token launch mistakes
Many legal failures in token launches are irreversible after issuance. The most common pattern is a founding team that treats compliance as a pre-launch task rather than a product design requirement, then discovers post-TGE that the cost of correction exceeds the cost of the original launch.
Core enforcement lesson: Enforcement actions involving Terraform Labs, Celsius, and BitMEX share a common thread: the gap between public representations and actual on-chain or operational controls. In each case, the legal exposure was created not by the token’s existence but by the inconsistency between what was promised and what was built. Founders who cannot demonstrate that their smart contract controls match their public decentralization claims face the same liability pattern, regardless of project size.
Common one-way-door mistakes and their consequences:
- Distributing tokens to U.S. persons without a valid securities exemption: triggers registration violations that cannot be cured by subsequent compliance
- Undisclosed admin keys or upgrade mechanisms: creates ongoing securities-law exposure and destroys exchange trust
- Marketing language promising returns: creates fraud liability that survives token failure
- Inadequate KYC/AML at launch: results in banking partner termination and exchange delisting, often simultaneously
- Inconsistent vesting disclosures: triggers investor claims and regulatory inquiries that are expensive to defend even when the project ultimately prevails
Practical remediation steps if you discover a post-launch compliance gap:
- Engage counsel immediately and do not make public statements about the gap before receiving legal advice
- Conduct a privileged internal review to assess the scope and legal consequences of the gap
- Preserve all relevant documents and communications; do not delete anything
- Assess whether voluntary disclosure to regulators is appropriate; early cooperation typically results in materially better outcomes
- Notify affected counterparties (exchanges, custodians) as required by contract
The benefits of early regulatory counsel are not theoretical. Projects that engage qualified securities and regulatory counsel before token design finalize their classification analysis, avoid the most common disclosure failures, and enter exchange diligence with a defensible compliance record. Projects that do not typically spend multiples of the original legal budget on remediation, defense, and settlement.
Murphyslawcrypto has litigated matters involving Celsius, Terraform Labs, and BitMEX, and maintains an active docket of enforcement defense and fraud recovery cases. That litigation experience directly informs the compliance guidance in this checklist: the mistakes that create the most expensive legal problems are consistently the ones that could have been avoided with early counsel.
Compliance is a product feature, not a pre-launch task
The conventional framing of token compliance as a checklist to complete before launch misses the more important point: compliance decisions made during product design determine the legal risk profile of the token for its entire lifecycle. A token designed with undisclosed admin controls, profit-expectation marketing, and inadequate KYC cannot be made compliant by adding disclosures after the fact. The architecture of the token is the compliance record.
Embedding compliance tasks in product sprints means that every smart contract design decision, every tokenomics parameter, and every marketing message is reviewed against the legal opinion before it ships. Counsel should be in the room when the token’s governance model is designed, not called in to review it after the whitepaper is published. That partnership between legal and engineering is what produces a token that can withstand institutional due diligence.
If your project is approaching TGE and any of the items in this checklist remain unresolved, the right move is to pause and engage counsel before proceeding. The cost of a delay is recoverable. The cost of an enforcement action, a delisting, or a class action is not.
Murphyslawcrypto’s compliance consulting and legal opinion services
Founders who have read this checklist and identified gaps in their compliance documentation have a clear next step: get a legal opinion and a readiness assessment from counsel with real enforcement experience in this space.
Murphyslawcrypto offers crypto compliance consulting specifically designed for token launch teams, covering legal opinion letters addressing token classification, KYC/AML program build-out and vendor coordination, audit-ready documentation review, custody and listing coordination, and regulatory defense if an inquiry arises post-launch. Unlike generic compliance vendors, Murphyslawcrypto brings active litigation experience from matters involving Celsius, Terraform Labs, and BitMEX directly to its compliance work, which means the advice reflects what regulators and plaintiffs actually look for, not what sounds good in a checklist.
To engage the firm, contact Murphyslawcrypto through Murphyslawcrypto with your project summary, current stage, target exchanges, and any existing legal opinions or audit reports. The intake team will assess your readiness gaps and propose a scope of engagement. Have your entity formation documents, whitepaper draft, and tokenomics model ready for the initial review.
Sources
The following primary sources and guidance documents are the ones founders and compliance teams should hand to counsel and counterparties:
- Application of FinCEN’s regulations to certain business models – FinCEN
- Investment Advisers Act rule release IA-5653 – SEC
- Law
This article is general information, not a substitute for advice from a qualified lawyer. Consult a qualified legal professional about your own circumstances before acting on anything here.
FAQ
What is the single most important item on a token launch compliance checklist?
A written, attorney-reviewed legal opinion addressing token classification under the Howey test is the single most important item. Without it, no Tier-1 exchange will list the token and no institutional custodian will onboard it.
When should a crypto project engage legal counsel for a token launch?
Counsel should be engaged before token design is finalized, ideally 12–18 months before the planned TGE. Engaging counsel after the whitepaper is published or the token contract is deployed leaves the most consequential compliance decisions already made and often irreversible.
Does a utility token still need KYC/AML controls?
Yes. KYC/AML controls are required at every touchpoint involving fiat currency, custodial relationships, or identifiable purchasers, regardless of whether the token is classified as a utility token. FATF guidance and FinCEN rules apply based on the activity, not the token’s label.
How long does custodian onboarding take for a new token?
Projects should initiate custodian outreach at least six months before TGE.
What happens if a compliance gap is discovered after token launch?
Engage counsel immediately and do not make public statements before receiving legal advice. Conduct a privileged internal review, preserve all documents, and assess whether voluntary regulatory disclosure is appropriate. Early cooperation with regulators consistently produces better outcomes than reactive defense.