
The Travel Rule requires virtual asset service providers to collect, verify, and transmit originator and beneficiary information alongside qualifying crypto transfers, then retain that data for regulators. Three frameworks govern how this plays out in practice: FATF Recommendation 16, the U.S. Bank Secrecy Act as enforced by FinCEN, and the European Union’s Transfer of Funds Regulation.
The thresholds differ sharply by jurisdiction, and that gap creates most of the compliance headaches operators face today.
- FATF baseline: a low-value threshold generally adopted by most member states
- EU Transfer of Funds Regulation: no threshold, requiring full data on every crypto transfer
- US Bank Secrecy Act precedent: $3,000 recordkeeping threshold under 31 CFR 1010.410
Quick fact: FATF revised Recommendation 16 in June 2025 specifically to standardize the information required above the USD/EUR 1,000 payment threshold and to push for better fraud and error protection tools industry-wide.
Key Takeaways
Travel Rule compliance succeeds when originator and beneficiary data collection, verification, and messaging are built to the strictest jurisdictional threshold a VASP touches, not the most convenient one.
| Point | Details |
|---|---|
| Core requirement | VASPs must collect, verify, and transmit originator and beneficiary data with qualifying transfers, then retain records. |
| Thresholds vary sharply | FATF sets a USD/EUR 1,000 baseline, the EU applies a zero threshold, and the US follows a $3,000 BSA precedent. |
| IVMS101 drives interoperability | This messaging schema lets different VASP systems exchange Travel Rule data in a common structured format. |
| Design to the strictest regime | Firms serving EU customers or counterparties should build zero-threshold compliance across their whole platform. |
| Legal risk hides in schema gaps | The interpretive gap between FATF R.15 and R.16 causes failures examiners can treat as noncompliance; Murphyslawcrypto helps firms close that gap before it becomes an enforcement matter. |
Table of Contents
- Who Must Comply With Crypto Travel Rule Requirements?
- What Data Fields Does the Travel Rule Require?
- How Do Travel Rule Thresholds Differ by Jurisdiction?
- How Does Travel Rule Messaging Actually Work?
- Building a Compliance Playbook: Verification, Screening, and Recordkeeping
- Why Do Travel Rule Transfers Get Rejected?
- What Happens if You Don’t Comply With the Travel Rule?
- A Quick Compliance Checklist for Travel Rule Readiness
- The Legal Reality Behind Travel Rule Compliance
- Get Travel Rule Compliance Right Before a Regulator Makes You
- Sources
- FAQ
Who Must Comply With Crypto Travel Rule Requirements?
Virtual Asset Service Providers, or VASPs, sit at the center of this obligation. The term covers exchanges, custodial wallet providers, OTC desks, and any business that conducts crypto transfers on behalf of customers as a business activity. In the EU, the equivalent term is CASP (Crypto Asset Service Provider) under MiCA. In the US, FinCEN generally treats these entities as Money Services Businesses (MSBs), layering crypto obligations onto existing BSA infrastructure.
That labeling difference matters more than it looks. A business licensed as a CASP in the EU faces the zero-threshold rule from day one, while a similar business registered as an MSB in the US operates under the $3,000 BSA precedent until crypto-specific rulemaking catches up. If you operate across both markets, you are effectively regulated by whichever regime is stricter, regardless of where your headquarters sits.
Custody status changes everything. When a VASP holds private keys for a customer, that transfer is straightforward: the VASP is either the ordering institution or the beneficiary institution, and Travel Rule obligations attach directly. Non-custodial or “unhosted” wallet transfers are murkier. Regulators increasingly expect VASPs to apply risk-based additional measures when a customer sends funds to or receives funds from a wallet the VASP doesn’t control, often requiring proof-of-ownership checks before the transfer clears above the applicable local threshold.
Multi-leg transfers add another layer of complexity. A transfer routed through an intermediary VASP, say a liquidity provider bridging two exchanges, creates three distinct roles:
- The ordering institution, which collects and verifies originator data
- The intermediary institution, which must pass all received data downstream unchanged
- The beneficiary institution, which must verify the data it receives before crediting the recipient
Each role carries independent liability. An intermediary that strips or truncates data to fit its own message format is not shielded just because it didn’t originate the transfer. The Crypto Travel Rule VASP Compliance framework treats the collect, transmit, and retain obligations as running through every hop in the chain, not just the first and last.
Edge cases you should map now: peer-to-peer transfers facilitated through a VASP’s interface, DeFi front ends operated by an identifiable legal entity, and self-hosted wallet withdrawals that later re-enter a custodial exchange. Regulators are increasingly scrutinizing whether a “decentralized” protocol has a controlling party that functions as a VASP in substance, even without that label.
What Data Fields Does the Travel Rule Require?
The FATF Travel Rule for crypto specifies two data sets depending on transfer size and jurisdiction: a full set for transfers above the applicable threshold, and a reduced set below it. Getting this wrong, either by collecting too little or by trusting an incomplete counterparty submission, is the single most common gap examiners find.
Full data set (above threshold):
- Originator’s full name
- Originator’s account number or wallet address used for the transaction
- Originator’s physical address, OR national identity number, OR customer identification number, OR date and place of birth (this is an “OR” choice, not a “collect all four” requirement)
- Beneficiary’s full name
- Beneficiary’s account number or wallet address
Reduced data set (below threshold, where a threshold applies):
- Originator’s name
- Beneficiary’s name
- Account numbers or unique transaction reference numbers for both parties
The “OR” language in the full data set trips up a lot of compliance teams building their intake forms. FATF doesn’t require you to capture a customer’s home address, national ID number, and date of birth all at once. It requires you to have at least one of those four identifiers on file and ready to transmit. Most VASPs standardize on national ID or passport number because it’s already collected during KYC onboarding, which avoids a second data-collection step at transfer time.
Verification expectations scale with risk and threshold. Below the reduced-data threshold, many jurisdictions only require that the information be available on request, not verified in advance. Above the full-data threshold, verification is generally mandatory before the funds move, not after. The EU’s zero-threshold approach under the Transfer of Funds Regulation removes this distinction entirely: every transfer, regardless of size, requires the full data set and pre-transfer verification.
IVMS101 has become the practical backbone for actually moving this data between VASPs. It’s a structured messaging schema, not a law, but it’s the format most Travel Rule solution providers use to encode originator and beneficiary fields into a machine-readable payload. Think of it as the common language that lets a compliance system built by one exchange talk to a completely different system built by a counterparty on the other side of a transfer. Without a shared schema like IVMS101, every VASP-to-VASP integration becomes a custom project, and custom projects are where compliance gaps hide.
None of this works if the underlying KYC data is thin. A VASP that onboarded customers with minimal identity verification has nothing solid to populate into these fields when a large transfer request comes in, which forces a choice between delaying the transfer or sending incomplete data and hoping the counterparty doesn’t reject it.
How Do Travel Rule Thresholds Differ by Jurisdiction?
Short answer: significantly, and the strictest jurisdiction you touch usually becomes your effective global standard. Here’s how the three major frameworks compare on legal force and dollar amount.
| Framework | Threshold | Legal Force | Practical Effect |
|---|---|---|---|
| FATF Recommendation 16 | USD/EUR 1,000 | Non-binding guidance for member states | Sets the global baseline most countries adopt into domestic law |
| EU Transfer of Funds Regulation | Zero threshold | Binding EU regulation, effective December 30, 2024 | Full data required on every crypto transfer processed by a CASP |
| US Bank Secrecy Act (31 CFR 1010.410) | $3,000 | Binding federal regulation | Long-standing wire transfer precedent; crypto-specific rulemaking still unsettled |
FATF itself doesn’t enforce anything directly. It sets recommendations that member countries are expected to transpose into domestic law, and it grades countries on their compliance through mutual evaluations. The USD/EUR 1,000 figure is the number most national regulators reference when writing their own Travel Rule statutes, but it’s a floor, not a ceiling, and several jurisdictions have gone well below it.
The EU didn’t just adopt the FATF baseline. It went further, and the Transfer of Funds Regulation eliminated the threshold entirely for crypto asset transfers processed by CASPs starting December 30, 2024. Every transfer, whether it’s $5 or $5 million, requires the full originator and beneficiary data set. That decision effectively exports EU compliance standards to any global VASP that wants EU customers or EU counterparties, because there’s no practical way to run two parallel compliance systems.
The US sits on older infrastructure. FinCEN hasn’t finalized a crypto-specific Travel Rule threshold separate from the general BSA wire-transfer recordkeeping requirement, which sits at $3,000 under 31 CFR 1010.410. Proposed rulemaking has floated changes, including a controversial 2020 proposal that would have lowered the threshold to $250 for transactions involving unhosted wallets, but nothing at that scale has been finalized. US-based VASPs currently operate under the $3,000 precedent while watching for further guidance.
Our practical advice, unambiguously: design your compliance architecture to the strictest regime you touch, not the most convenient one. If you serve EU customers or route transfers through EU counterparties, build for zero threshold across your entire platform. Retrofitting a US-centric system to handle EU-grade data collection after the fact costs more in engineering hours and legal exposure than building it correctly the first time. Jurisdictions with stricter floors, including several APAC markets, tend to set the de facto compliance standard for any VASP with cross-border ambitions.
How Does Travel Rule Messaging Actually Work?
Data doesn’t move between VASPs by email or a shared spreadsheet, at least not in any system that would survive an audit. It moves through structured messaging protocols built around a common schema, and the choices you make here determine whether your compliance program is fast and reliable or a constant source of rejected transfers.
IVMS101 is the schema most of the industry has converged on for structuring these payloads. It defines exactly how originator name, address, and identification fields get encoded so that a message sent from one VASP’s system arrives readable and complete at another VASP’s system, even if the two platforms were built independently. Most commercial Travel Rule solutions support IVMS101 natively, which is part of why it has become the de facto standard rather than a mandated one.
Where VASPs differ is in how they actually exchange these messages:
- Direct peer-to-peer messaging between VASPs, where each institution integrates directly with its counterparties. This offers the most control and the least third-party data exposure, but it doesn’t scale well past a handful of regular counterparties.
- Hub or network-based solutions, where multiple VASPs connect to a shared intermediary that routes and translates messages. This scales faster and reduces the number of individual integrations needed, but it introduces a third party that touches sensitive customer data.
- Translation or gateway services, which sit between incompatible systems and convert one VASP’s message format into another’s. Useful for bridging legacy systems, but every added hop is another point of latency and potential data leakage.
Each model trades off latency, privacy, and reliability differently, and most mid-sized VASPs end up running a hybrid: direct connections with their top counterparties, and a hub solution for the long tail of smaller or occasional partners.
Whichever model you choose, the security controls underneath it are non-negotiable:
- End-to-end encryption for data in transit and at rest
- Strict key management with rotation policies and access controls limited to compliance personnel
- Complete access logs showing who viewed or transmitted customer data and when
- Auditable trails that reconstruct the full data path for any given transfer on request
Pro Tip: Test your IVMS101 message exchange with a live counterparty before you ever process a real customer transfer through it. Schema mismatches that look fine in documentation frequently break in practice, whether that’s a truncated field, a missing required element, or a character encoding issue that corrupts non-Latin names.
Building a Compliance Playbook: Verification, Screening, and Recordkeeping
A working Travel Rule program is less about the rule itself and more about the operational scaffolding around it. Four pieces need to work together: identity verification, sanctions screening, recordkeeping, and a clear policy for what happens when data is missing.
-
Map your KYC data to Travel Rule fields, and assign clear system ownership. The name, ID number, and address you collect during onboarding needs to flow automatically into your Travel Rule messaging system when a qualifying transfer occurs. If that mapping is manual, someone on your team is retyping customer data under time pressure, and that’s where transcription errors and compliance gaps creep in. Assign one system or team as the source of truth for identity data, and make every downstream process pull from it rather than maintaining parallel copies.
-
Build real-time sanctions and AML screening into the transfer workflow, not after it. Screening the originator and beneficiary against OFAC, UN, and other applicable sanctions lists needs to happen before funds move, not as a post-transaction audit step. Set a clear internal SLA, many firms target screening resolution within minutes for automated matches and same-day resolution for flagged transfers requiring manual review. A tool built for AI-assisted sanctions screening can help compress that window without adding headcount, though the underlying screening list and escalation policy still need human ownership.
-
Define recordkeeping requirements before an examiner asks for them, not during the exam. At minimum, retain the full originator and beneficiary data set, the transfer amount and timestamp, the messaging protocol used, and any screening results, for the retention period your jurisdiction requires. Examiners expect to see a clean, reconstructable audit trail for any transfer you flag as compliant, and gaps in that trail are treated the same as gaps in the underlying data collection.
-
Write a firm policy for missing or incomplete data before you need it. Decide in advance: how long will you hold a transfer waiting for a counterparty to supply missing fields, what threshold of missing data triggers an automatic rejection, and who has authority to approve an exception. Without a written policy, this decision gets made ad hoc by whoever is on shift when the transfer comes in, and inconsistent handling is exactly what regulators flag during exams.
Pro Tip: Run a quarterly “missing data” audit on rejected and delayed transfers. If the same counterparty VASP keeps triggering your exception queue, that’s a signal to either escalate the relationship at the compliance level or reconsider whether you should keep routing volume through them.
Our crypto compliance guide for businesses covers documentation standards that pair directly with these four pillars, and assigning clear ownership under a defined compliance officer role is what keeps this playbook from decaying into ad hoc firefighting six months after launch.
Why Do Travel Rule Transfers Get Rejected?
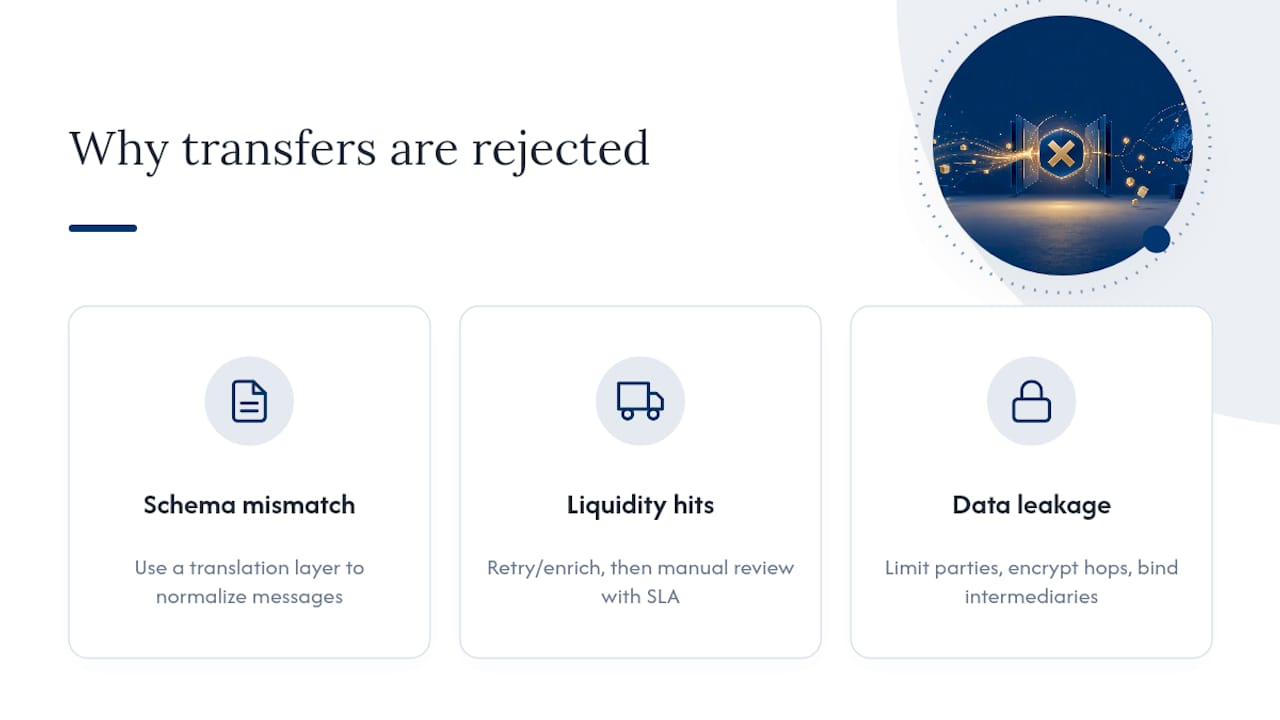
Three problems account for most of the operational pain compliance teams report: schema mismatches, liquidity disruption from rejected transfers, and the tension between transparency obligations and data minimization.
Schema mismatches happen because banking rails and crypto rails were built by different industries with different assumptions baked in. A bank wire message format doesn’t map cleanly onto a crypto transfer’s data structure, and even within crypto, not every VASP has adopted IVMS101 in the same way. The result is a transfer that looks complete on the sending side and arrives malformed or incomplete on the receiving side. There’s an enduring interpretive gap between how FATF’s Recommendation 15 extends obligations to VASPs and how Recommendation 16 defines the actual data requirements, and that gap shows up as inconsistent field expectations across implementations. The practical fix is a dedicated translation layer that normalizes incoming and outgoing messages against a single internal schema, rather than trying to hand code every counterparty integration separately.
Rejected transfers disrupt liquidity fast. A customer trying to move funds for a time-sensitive trade doesn’t care that your compliance system flagged a missing beneficiary field. Build a retry-and-exception workflow rather than a hard reject: attempt automatic data enrichment first (pulling from a prior successful transfer with the same counterparty, for instance), then route to manual review with a defined SLA, and only reject outright after both steps fail. This keeps legitimate customer transfers moving while still holding the line on incomplete data.
Data leakage risk cuts against the transparency the rule demands. Every additional party that touches originator and beneficiary data, whether that’s a messaging hub, a translation service, or an intermediary VASP, is another point where sensitive customer information could be exposed or misused. The fix isn’t to withhold required data; that just creates a different compliance failure. It’s to minimize the number of parties who see more than they need, encrypt data in transit at every hop, and contractually bind every intermediary to the same retention and access standards you hold yourself to.
What Happens if You Don’t Comply With the Travel Rule?
FinCEN treats recordkeeping failures as material violations of the Bank Secrecy Act, and the agency has a documented enforcement history against institutions that failed to collect or transmit required originator and beneficiary information. Civil penalties for BSA recordkeeping violations can be substantial, and repeated or systemic failures tend to draw harsher scrutiny than a single isolated gap.
In the EU, national supervisory authorities enforce the Transfer of Funds Regulation, and CASPs operating across multiple member states face compounded exposure: a compliance gap identified by one national regulator can trigger scrutiny from others, particularly where the same failure pattern shows up across a firm’s entire EU footprint.
Certain red flags should move you straight to legal counsel rather than an internal fix:
- Systemic data collection failures affecting a large share of transfers, not an isolated incident
- Repeated gaps in the same failure category after a prior remediation attempt
- Any indication that missing data or a stripped message could be connected to sanctions evasion
- A regulator inquiry or examination request that references Travel Rule recordkeeping specifically
The gap between what a compliance policy says on paper and what your transaction logs actually show is where most enforcement cases get built. Regulators don’t need to prove intent to hold a firm liable for BSA recordkeeping failures. They need the gap.
If you receive a regulator inquiry referencing Travel Rule compliance, your first move should be preserving every relevant record, communication, and system log before you respond, not after. Our guide on responding to a crypto regulatory inquiry walks through how to protect privilege while still cooperating in good faith, which is a harder balance than it sounds under time pressure.
A Quick Compliance Checklist for Travel Rule Readiness
Run this as a working session with your compliance and engineering leads together, not as a document one team fills out in isolation.
- Inventory every transfer flow, counterparty type, and applicable threshold. List every jurisdiction you operate in or serve customers from, and note which threshold (FATF baseline, EU zero-threshold, US $3,000) actually governs each flow.
- Choose your messaging model and test it end to end. Decide between direct VASP-to-VASP messaging, a hub solution, or a hybrid, then run a live IVMS101 exchange with at least one real counterparty before processing production transfers through it.
- Wire KYC data directly into your Travel Rule pipeline. Confirm that originator and beneficiary fields populate automatically from your existing identity verification system rather than requiring manual entry at transfer time.
- Enable real-time sanctions screening with a defined resolution SLA. Set clear timelines for automated clears and manual escalations, and document who owns the final call on a flagged transfer.
- Write your retention and incident-response policies before you need them. Define how long records are kept, what a “missing data” exception looks like, and who has authority to approve it.
- Train frontline compliance staff and schedule a tabletop exercise. Walk through a simulated regulator inquiry or a mock rejected-transfer scenario so your team isn’t improvising the first time it happens for real.
A checklist like this only holds up if someone owns it past launch day. Building recurring internal audits into your calendar, quarterly at minimum, is what separates a Travel Rule program that survives an exam from one that just looks good in a policy binder.
The Legal Reality Behind Travel Rule Compliance
Most compliance guides treat the Travel Rule as a technical problem: collect the right fields, pick a messaging vendor, done. That framing misses where the actual legal exposure lives.
FATF extends Travel Rule obligations to VASPs through its Interpretive Note to Recommendation 15, not directly through Recommendation 16 itself. That’s not a technicality. It means the specific data requirements VASPs must meet were never written with crypto messaging architecture in mind, which is exactly why schema mismatches between banking rails and crypto rails keep surfacing in enforcement matters. When a firm’s system fails to reconcile that gap cleanly, the resulting data failure looks, to an examiner, indistinguishable from willful noncompliance.
We’ve seen this pattern before in adjacent enforcement contexts: a technical integration failure that a firm treats as an engineering bug becomes, in a regulator’s hands, evidence of inadequate program design. The firms that fare best under examination are the ones that can produce a clean paper trail showing they understood the interpretive gap and built deliberate controls around it, not the ones who simply had good intentions.
Two governance habits do more to limit exposure than any single technology choice: documenting every policy decision on missing-data handling with a timestamp and a named decision maker, and running periodic internal audits that mirror what an examiner would actually request. Firms that wait until an inquiry arrives to organize their records are already behind. If your program has gaps you can’t explain confidently, that’s the signal to bring in compliance consulting before a regulator forces the conversation.
— Mark
Get Travel Rule Compliance Right Before a Regulator Makes You
Murphyslawcrypto is the counsel crypto businesses call when Travel Rule compliance stops being a policy document and starts being a real operational and legal exposure. Founded by Liam Murphy, who has litigated matters involving Celsius, Terraform Labs, and BitMEX, the firm builds compliance programs that hold up under examination, not just on paper.
If you’re standing up Travel Rule infrastructure for the first time, retrofitting a system after an EU expansion, or facing a regulator inquiry that references recordkeeping gaps, the earlier you bring in counsel, the more options you have. Murphyslawcrypto’s crypto compliance consulting service works directly with your compliance and engineering teams to close the interpretive and schema gaps that create enforcement risk, and the firm’s crypto compliance guide for businesses is a useful starting reference for what examiners expect to see. If you’re already facing a regulatory inquiry, don’t wait for the next letter to arrive. Reach out to discuss your specific exposure before you respond to the regulator.
Sources
For the primary texts behind everything covered here, go straight to the source documents rather than secondhand summaries:
This article is general information, not a substitute for advice from a qualified lawyer. Consult a qualified legal professional about your own circumstances before acting on anything here.
FAQ
What Is the Travel Rule in Crypto?
The crypto Travel Rule requires VASPs to collect, verify, and transmit originator and beneficiary information alongside qualifying virtual asset transfers, then retain those records for regulators to review.
Does the Travel Rule Apply to Cryptocurrency?
Yes. FATF extended the Travel Rule to virtual assets through its Interpretive Note to Recommendation 15 in 2019, and most jurisdictions have since built crypto-specific implementing rules, including the EU’s Transfer of Funds Regulation.
What Are the Limits for Crypto Travel Rule Thresholds?
FATF’s non-binding baseline is USD/EUR 1,000, the EU applies a zero threshold requiring full data on every crypto transfer, and the US follows a $3,000 recordkeeping threshold under the Bank Secrecy Act.
Does the 30 Day Rule Apply to Crypto?
The “30 day rule” is a tax concept used in some jurisdictions for cost-basis and wash-sale style calculations, not a Travel Rule requirement; it governs how gains are calculated, not what data must accompany a transfer.
Who Enforces Travel Rule Compliance for Crypto Businesses?
In the US, FinCEN enforces Bank Secrecy Act recordkeeping obligations, while EU national supervisory authorities enforce the Transfer of Funds Regulation; firms facing an inquiry from either should involve compliance counsel like Murphyslawcrypto early to preserve privilege and organize records properly.