
A crypto licensing gap occurs when a firm holds a formal license but lacks the operational, technical, or governance controls that regulators expect in day-to-day operations. The license grants market access. It does not build your AML program, tune your transaction monitoring, or segregate client assets. That gap between permission and readiness is where enforcement actions are born.
If you suspect your firm has a licensing gap, three triage actions matter immediately:
- Pause new customer onboarding in any product line where your KYC/AML controls are unverified or untested.
- Run an AML rule sweep to confirm your transaction monitoring system is active, tuned to your actual transaction volumes and risk profile, and generating alerts that a human reviews.
- Identify your primary regulators and check notification obligations. FinCEN requires Money Services Business registration and ongoing BSA compliance; a gap in suspicious activity reporting triggers direct enforcement risk. The SEC may assert jurisdiction over any token your firm issues, trades, or custodies that it considers a security. Your state regulator (for example, NYDFS under the BitLicense framework) may have independent examination authority and its own operational standards that run parallel to federal requirements.
None of those three actions requires outside counsel to start. All three create the documentation trail that counsel will need if a regulator calls first.
Key Takeaways
A crypto licensing gap is the distance between what a license permits and what regulators find when they examine your actual operations — closing it requires documented, tested controls, not policy documents.
| Point | Details |
|---|---|
| License is a starting line | Formal authorization grants market access but does not build AML, custody, or governance controls. |
| Triage immediately | Pause onboarding in unverified product lines and run an AML rule sweep within 48 hours of identifying a gap. |
| Score yourself honestly | Use the Red/Amber/Green rubric across eight control areas to identify your highest-priority remediation targets. |
| Remediation takes months | Full program build with audited controls typically requires 6–18 months; triage can begin in 48 hours. |
| Murphyslawcrypto | Offers fixed-scope gap assessments, AML program builds, and regulatory defense for licensed firms facing enforcement risk. |
Table of Contents
- What a crypto license actually authorizes vs. what operating compliantly requires
- Where licensing gaps show up in practice
- Why licensing gaps persist in the United States
- What it costs your business to ignore a licensing gap
- How to close a crypto licensing gap: a prioritized checklist
- How ready is your firm? A practical scorecard
- What enforcement actions teach about licensing gaps
- When to bring in specialized legal or compliance counsel
- A compliance and enforcement lawyer’s perspective on what actually matters
- Murphyslawcrypto closes licensing gaps before regulators find them
- Sources
- FAQ
What a crypto license actually authorizes vs. what operating compliantly requires
A crypto license is formal regulatory permission to provide defined crypto services in a defined jurisdiction. What it authorizes and what it demands are two different things.
What a license typically grants:
- Permission to operate as a money transmitter, exchange, custodian, or broker-dealer (depending on license type and jurisdiction)
- Access to regulated banking and payment rails that require a licensed counterparty
- The right to publicly represent your firm as authorized to provide specific services
- In some frameworks, passporting rights to operate across multiple states or countries without separate applications
What operating compliantly actually requires, every day:
- A functioning AML/KYC program with documented risk ratings, customer due diligence procedures, and enhanced due diligence for high-risk accounts
- Transaction monitoring software tuned to your specific product, transaction types, and customer base, with a human review process for alerts
- Sanctions screening against OFAC’s SDN list and other applicable lists, applied at onboarding and on an ongoing basis
- Segregation of client assets from firm assets, with reconciliation cadences documented and auditable
- Governance structures: a designated BSA/AML compliance officer, written policies, board-level oversight, and documented training records
- Audited or examined financial statements, depending on license category
- Incident response procedures that include regulator notification timelines
The distinction between license categories sharpens this gap considerably. Registrations and full authorizations operate at different levels of scrutiny. A FinCEN MSB registration is procedural: you file, you are registered, and you bear the full burden of building BSA-compliant controls yourself with no substantive regulator review of your program before you go live. A full authorization, such as the New York BitLicense or a CASP authorization under MiCA, involves substantive regulator review of your program before approval. That review creates a higher baseline expectation. Firms that treat a registration as equivalent to an authorization routinely discover the gap during their first examination.
FINRA adds another layer for broker-dealer members: crypto assets may or may not be securities, and member firms engaging in crypto-asset activities are expected to notify FINRA and apply existing supervisory and securities rules where applicable. A firm that holds a state money transmitter license but also operates a token trading desk without notifying FINRA has a gap that no state license closes.
Where licensing gaps show up in practice
Most firms do not discover their gaps in a policy review. They discover them during an examination, a banking partner audit, or an enforcement inquiry. The failure modes cluster in predictable areas.
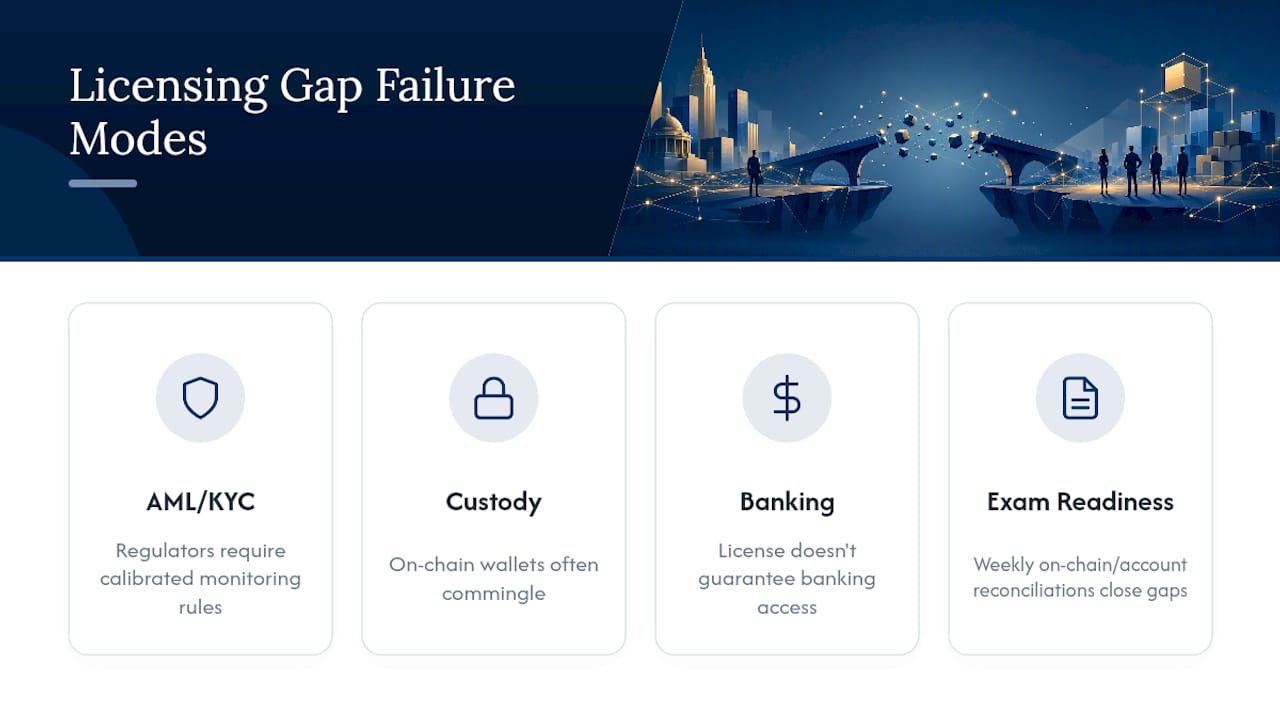
AML/KYC and transaction monitoring. The most common gap. Firms implement a monitoring system at launch, set generic rule thresholds, and never retune them as transaction volumes, customer types, or product features change. Regulators test whether your rules are calibrated to your actual risk, not whether you have a system installed.
Custody and client asset segregation. Licensed custodians and exchanges frequently commingle operational wallets with client asset wallets at the infrastructure level, even when accounting entries show segregation. Regulators and bankruptcy trustees both look at on-chain wallet architecture, not just ledger entries.
Banking and fiat rails. A license does not guarantee a bank account. Bank de-risking has forced many licensed crypto firms into correspondent banking arrangements that introduce their own compliance obligations and operational fragility. Losing a banking partner mid-operation is an operational gap that a license cannot prevent.
Vendor and partner integrations. Your custodian, liquidity provider, and KYC vendor each carry their own compliance obligations. If your custodian’s controls fail, your regulator may hold you responsible for the downstream gap. Vendor contracts should include compliance representations, audit rights, and incident notification obligations.
Reporting and exam readiness. Many firms cannot produce, on short notice, a complete transaction history with counterparty identifiers, a current AML risk assessment, or a reconciliation between on-chain addresses and accounting records. Exam readiness is an operational state, not a document you prepare after a subpoena arrives.
Governance, personnel, and documented policies. A BSA officer title without authority, budget, or board access is a governance gap. Regulators examine whether the compliance function has genuine independence and resources, not just an org chart entry.
Reserves, audits, and financial reporting. Proof-of-reserves attestations and audited financials are distinct requirements. Firms that conflate them, or that have neither, face heightened scrutiny from both regulators and institutional counterparties.
Pro Tip: End-to-end reconciliation between on-chain custody addresses and your accounting ledger, run on a documented weekly cadence, closes multiple gaps simultaneously: it satisfies custody segregation evidence requirements, supports your reserves attestation, and creates the audit trail regulators expect during examinations.
Why licensing gaps persist in the United States
The U.S. regulatory structure for crypto is not a single framework. It is a layered, partially overlapping set of federal and state regimes with no passporting mechanism and no single authoritative regulator.
The 50-state patchwork. Operating nationally means holding money transmitter licenses (MTLs) in most states, plus separate virtual currency licenses where states have enacted them. New York’s BitLicense, for example, imposes operational requirements that go well beyond a standard MTL: cybersecurity standards, consumer protection rules, and capital requirements that a FinCEN MSB registration does not address. A firm licensed in 40 states may still be operating unlicensed in the remaining 10 while its transaction monitoring covers all 50.
Federal ambiguity and enforcement patchiness. FinCEN’s BSA framework applies to MSBs and focuses on AML/KYC. The SEC asserts jurisdiction over tokens it considers securities and has pursued enforcement actions against exchanges, issuers, and custodians on that basis. The CFTC claims authority over crypto derivatives and spot commodity markets. No single federal agency has comprehensive jurisdiction, and the agencies do not always coordinate. A firm that satisfies FinCEN’s BSA requirements may still face an SEC enforcement action for custody or offering practices.
Bank de-risking. Licensed crypto firms routinely lose banking relationships because correspondent banks apply their own risk assessments independent of any license. The result is operational gaps: delayed fiat settlements, inability to process customer withdrawals, and forced reliance on payment processors with their own compliance requirements. A license does not compel a bank to maintain the relationship.
Evolving federal signals. The GENIUS Act, which addresses stablecoin issuance and federal oversight, represents one of the more concrete federal legislative signals in years. But its rulemaking timeline remains uncertain, and divergent frameworks between U.S. proposals and regimes like MiCA create structural interoperability gaps for firms operating across jurisdictions. A firm compliant under one regime may still be non-compliant under another, forcing parallel compliance tracks that multiply operational cost and complexity.
What it costs your business to ignore a licensing gap
The consequences of an unaddressed licensing gap are not theoretical. Regulators act quickly on AML and custody failures, and the outcomes range from expensive to existential.
Direct regulatory penalties. FinCEN has assessed civil money penalties in the tens of millions of dollars against crypto firms for BSA violations. The SEC has obtained injunctions, disgorgement orders, and civil penalties in enforcement actions against exchanges and issuers. State regulators, including NYDFS, have revoked licenses and imposed consent orders that restrict business operations for years. Individual executives face personal liability, including criminal referrals, when compliance failures are willful or egregious.
Enforcement reality: Regulators act quickly on AML/monitoring and custody failures. Firms that obtain licenses but fail in day-to-day controls still face rapid supervisory action — the license does not create a grace period for operational readiness.
Operational consequences. Loss of banking relationships forces operational restructuring under pressure. Custodial freezes during an enforcement investigation can prevent clients from accessing their assets, triggering civil litigation on top of regulatory proceedings. Forced wind-downs require expensive client asset transfer processes, often under court supervision. Reputational damage from public enforcement actions accelerates client churn in ways that are difficult to reverse.
Pro Tip: If you receive a regulator inquiry or subpoena, preserve all relevant records immediately and do not alter, delete, or migrate data pending legal review. Evidence preservation in the first 48 hours is the single highest-leverage action available to limit enforcement exposure.
How to close a crypto licensing gap: a prioritized checklist
Remediation follows a three-phase sequence. Immediate containment first, then controls remediation, then external validation.
Phase 1: Immediate containment (48–72 hours)
- Pause onboarding in any product line with unverified KYC/AML controls.
- Preserve all transaction records, monitoring logs, and regulator correspondence.
- Identify the specific licenses held, their conditions, and any outstanding regulator commitments.
- Confirm your BSA/AML compliance officer has current authority and is actively engaged.
Phase 2: Controls remediation (weeks to months)
- Retune transaction monitoring rules against your current transaction volume, customer risk tiers, and product features. Use synthetic test vectors, including on-chain test cases, to validate that rules fire correctly before going live.
- Implement or verify sanctions screening against OFAC’s SDN list at onboarding and on a real-time basis for transactions.
- Audit custody wallet architecture to confirm on-chain segregation of client assets from operational wallets, and document the reconciliation cadence.
- Review all vendor contracts for compliance representations, audit rights, and incident notification clauses.
Phase 3: Program build and external validation (months to 18 months)
- Commission an independent AML program review or examination-readiness assessment.
- Build or update governance documentation: board-level compliance oversight, written BSA/AML policies, training records, and a documented incident response procedure.
- Obtain audited financials or proof-of-reserves attestations appropriate to your license category.
- Establish a regulator communication protocol so that any inquiry is routed to legal and compliance before a business-line response goes out.
Owners by function:
- Legal/GC: license condition review, regulator correspondence, evidence preservation
- Compliance officer: AML program, monitoring tuning, sanctions screening, governance documentation
- CTO/Engineering: custody wallet architecture, monitoring system integration, synthetic test vectors
- CFO: audited financials, reserves attestation, banking relationship management
Pro Tip: Align engineering and compliance on transaction-monitoring tuning by running synthetic test vectors, including on-chain test cases that simulate structuring, layering, and sanctions-adjacent transactions. This produces documented evidence that your rules work, which is exactly what regulators ask for in an examination.
For a detailed crypto compliance program framework, the Murphyslawcrypto compliance guide covers each phase with specific control checklists.
How ready is your firm? A practical scorecard
Score each control area Red (not in place), Amber (partially implemented), or Green (documented, tested, and auditable).
| Control Area | Red | Amber | Green |
|---|---|---|---|
| AML/KYC program documented and tested | No written program | Written but not tested | Tested, tuned, and reviewed annually |
| Transaction monitoring rules calibrated | Generic/default rules | Rules set at launch, not retuned | Retuned to current risk profile, test vectors run |
| Client asset custody segregated on-chain | Commingled wallets | Accounting segregation only | On-chain segregation with weekly reconciliation |
| Audited financials or reserves attestation | Neither in place | Attestation only | Full audit completed |
| Banking relationships stable | No bank account | Single banking partner | Multiple relationships with documented contingencies |
| Governance: BSA officer, board oversight | No designated officer | Officer named, no board access | Officer with authority, budget, and board reporting |
| Vendor contracts with compliance clauses | No compliance terms | Partial coverage | All key vendors with audit rights and notification clauses |
| Exam readiness: records producible in 72 hours | Cannot produce | Partial records available | Full records producible with documented retrieval process |
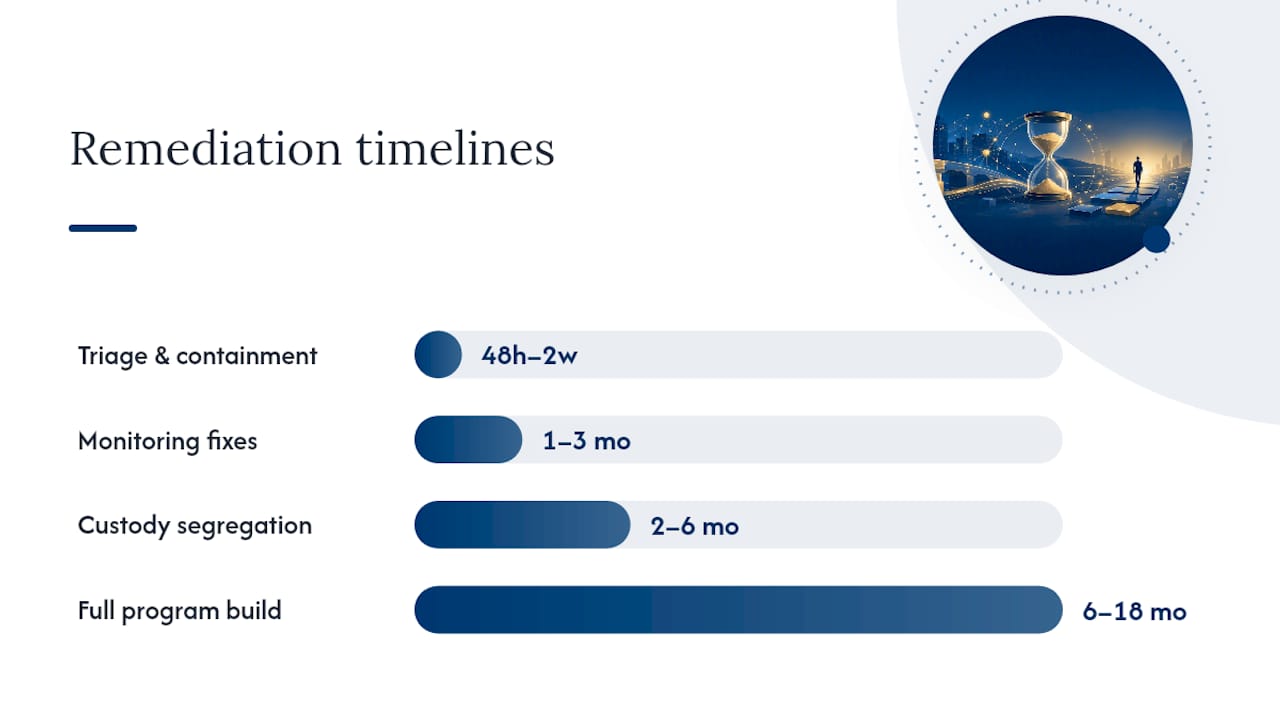
Typical remediation timelines:
- Triage and immediate containment: 48 hours to 2 weeks
- Transaction monitoring and sanctions screening fixes: 1–3 months
- Custody segregation engineering: 2–6 months
- Full program build with governance and audited controls: 6–18 months
Ballpark cost bands vary significantly by firm size and complexity. Transaction monitoring vendor implementation and tuning typically runs from tens of thousands to low six figures. Custody segregation engineering work at a mid-size exchange can reach six figures. Independent AML program reviews and legal/regulatory consulting for a full remediation engagement commonly range from low to mid six figures, depending on scope and whether enforcement is active. These are conservative ranges; costs scale with transaction volume, number of jurisdictions, and the severity of existing gaps.
The role of a compliance officer in managing this scorecard and driving remediation timelines is covered in detail in the Murphyslawcrypto compliance officer guide.
What enforcement actions teach about licensing gaps
Three enforcement patterns account for the majority of regulatory actions against licensed crypto firms.
AML and transaction monitoring failures. Regulators have repeatedly found that licensed firms ran transaction monitoring systems that were never tuned after initial deployment, generated alerts that no one reviewed, or applied rules designed for fiat transactions to crypto without adjustment. The pattern in enforcement: the firm had a system, the system was not working, and the firm represented to regulators that it had a functioning AML program. That gap between representation and reality drives the most serious outcomes, including criminal referrals for individual executives.
Custody breaches and asset commingling. Several high-profile insolvencies revealed that firms representing themselves as custodians were commingling client assets with operational funds. When insolvency proceedings began, the on-chain wallet architecture told a different story than the accounting records. Bankruptcy trustees and regulators both used on-chain forensic analysis to reconstruct the actual custody picture. The lesson: custody representations to clients and regulators must match the on-chain reality, not just the ledger.
Misleading public statements about coverage or insurance. Firms that represented client assets as insured or protected under a specific regulatory framework, when that coverage was limited or nonexistent, have faced both regulatory enforcement and civil litigation from clients. The gap between marketing language and actual regulatory protection is a recurring source of liability.
The pattern across these enforcement actions is consistent: the licensing gap is not the absence of a license. It is the distance between what the license implies and what the firm can actually demonstrate operationally. Regulators prioritize demonstrable, operational evidence: tuned AML rules, documented governance decisions, and reproducible custody reconciliations are more persuasive in examinations than high-level policy documents alone.
MiCA’s experience reinforces this pattern. By mid-2025, multiple EU national regulators had issued CASP licenses, and the operational requirements around audited statements and segregation drove acquisition and entity-restructuring decisions at firms that had not built those controls before applying. The license created the obligation; the gap was in the operational infrastructure to meet it.
For U.S. firms, the SEC’s enforcement approach to custody and token offerings follows a similar logic: the agency looks at what a firm actually does, not what its license category suggests it should be doing.
When to bring in specialized legal or compliance counsel
Some gaps you can close internally. Others require outside counsel before you take another operational step.
Red flags that require counsel immediately:
- A regulator inquiry, civil investigative demand, or subpoena has arrived.
- An enforcement action or asset freeze is active or threatened.
- Your custody architecture cannot be reconciled with your client-facing representations.
- You have significant client asset exposure and no clear segregation documentation.
- A banking or custodial partner has terminated or threatened to terminate the relationship citing compliance concerns.
What to bring to the first counsel call:
- Copies of all licenses held, including conditions and any outstanding commitments
- Your current AML program document and the last date it was reviewed
- Transaction monitoring system documentation, including rule logic and alert review records
- Custody architecture diagrams showing wallet structure and segregation
- Any regulator correspondence, examination reports, or consent orders
- Bank correspondence related to de-risking or account termination
Questions to ask in the first call:
- What is the realistic enforcement risk given the specific gap, and what is the likely timeline if a regulator is already engaged?
- What immediate stop-gap measures reduce exposure in the next 72 hours?
- What evidence should be preserved now, and what should not be altered or migrated?
- What is the recommended engagement structure and cost estimate for remediation?
Pro Tip: Structure the initial engagement as a fixed-fee scoping review, typically covering license condition analysis, gap identification, and a prioritized remediation roadmap. This gives you a defined deliverable and cost before committing to a broader remediation engagement. Subsequent work can be structured as capped or blended billing, which aligns counsel’s incentives with efficient remediation rather than hourly accumulation.
Early regulatory counsel consistently reduces both enforcement risk and total remediation cost. The Murphyslawcrypto guide on early counsel engagement explains why the timing of that decision matters as much as the decision itself.
A compliance and enforcement lawyer’s perspective on what actually matters
The most common mistake licensed crypto firms make is treating the license application as the compliance program. They invest heavily in the application, hire outside counsel to navigate the approval process, and then assume the approved application document is the operational baseline. It is not. Regulators approved your application based on representations about what your program would look like. They examine you based on what it actually looks like, in production, under real transaction volumes.
The second most common mistake is governance in name only. A BSA officer who lacks budget authority, cannot escalate to the board, and has no documented record of compliance decisions is not a compliance function. It is a title. When enforcement counsel reviews governance in discovery, they look for evidence that compliance had real authority: board minutes referencing compliance reports, documented escalations, written records of decisions made and overridden. The absence of that paper trail is itself evidence of a gap.
What actually moves regulators toward resolution rather than escalation is demonstrable operational evidence. Tuned monitoring rules with test documentation. Custody reconciliations with timestamps. Governance decisions in writing. Firms that can produce that evidence quickly, in response to an examination request or a subpoena, consistently reach better outcomes than firms that produce polished policy documents with no operational substance behind them.
Murphyslawcrypto closes licensing gaps before regulators find them
Murphyslawcrypto, founded by Liam Murphy, Esq. (Penn Law, formerly Paul Hastings, Selendy Gay, and McKool Smith), brings litigation-tested compliance experience to crypto businesses that need more than a policy document. The firm has worked on enforcement matters involving Celsius, Terraform Labs, and BitMEX, which means the compliance advice comes from counsel who has seen how these gaps play out in discovery, in receivership, and in front of regulators.
For licensed crypto businesses facing a gap, Murphyslawcrypto offers fixed-scope compliance assessments, AML program builds and transaction-monitoring tuning, custody architecture reviews, and full regulatory defense when enforcement is active or threatened. The first 72 hours of engagement focus on evidence preservation, immediate exposure triage, and a prioritized remediation roadmap, so your team knows exactly what to fix and in what order.
If your firm is licensed but uncertain whether its operational controls match what regulators will find in an examination, the right step is a structured assessment before the examination request arrives. Contact Murphyslawcrypto through the crypto compliance consulting page to schedule an initial scoping call.
Sources
These regulator pages and authoritative summaries are the primary references for U.S. crypto compliance obligations:
- FINRA — Crypto assets (key topics)
- Why Crypto’s Regulatory Gap Is Now an Institutional Problem – FinTech Weekly
- Types of Crypto Licenses Explained 2026 | Paybis
- Cryptolicenses
This article is general information, not a substitute for advice from a qualified lawyer. Consult a qualified legal professional about your own circumstances before acting on anything here.
FAQ
What is a crypto licensing gap in plain terms?
A crypto licensing gap is the difference between holding a formal regulatory license and actually operating with the controls regulators expect. A license grants permission; it does not build your AML program, custody architecture, or governance structure.
Does a FinCEN MSB registration satisfy U.S. crypto compliance requirements?
No. FinCEN MSB registration is a procedural filing that triggers BSA obligations, including AML program requirements and SAR filing. It does not substitute for state money transmitter licenses, SEC registration where securities are involved, or the operational controls regulators examine.
Can the IRS see your crypto wallet?
Yes. The IRS uses blockchain analytics tools and receives transaction data from exchanges through reporting and summons authority. On-chain transactions are pseudonymous, not anonymous, and regulators and law enforcement routinely trace wallet activity.
What triggers an SEC enforcement action against a licensed crypto firm?
The SEC typically acts when a firm issues, trades, or custodies tokens the agency considers securities without registering as a broker-dealer, exchange, or investment adviser. Holding a state money transmitter license does not provide a defense to SEC jurisdiction over securities activities.
When should a crypto business hire outside legal counsel for a licensing gap?
Hire counsel immediately if you receive a regulator inquiry, subpoena, or enforcement notice, or if your custody architecture cannot be reconciled with your client-facing representations. For proactive remediation, early engagement consistently reduces both enforcement risk and total remediation cost.