
On-chain forensics is the discipline of tracing, analyzing, and documenting cryptocurrency transactions on a public blockchain to produce evidence suitable for legal proceedings, criminal investigations, and regulatory compliance. According to Chainalysis, the structured forensic workflow moves from data collection through address clustering, entity attribution, transaction graph analysis, and cross-chain tracing to final evidence documentation, with Daubert-standard relevance built into the methodology. Immediate use cases span law enforcement investigations, AML/KYC compliance, civil fraud recovery, and incident response. OFAC sanctions screening and chain-of-custody documentation are standard outputs, not optional add-ons.
The term “on-chain forensics” is sometimes used interchangeably with blockchain analytics, but the two disciplines have different purposes and different evidentiary standards. Understanding that distinction, and knowing when to escalate from monitoring to a full forensic investigation, is what separates a useful alert from a court-ready report.
Key Takeaways
On-chain forensics produces court-ready evidence by combining address clustering, entity attribution, and chain-of-custody documentation, and its output is only as useful as the legal strategy it supports.
| Point | Details |
|---|---|
| Core definition | On-chain forensics traces and documents blockchain transactions to produce evidence for legal proceedings and compliance. |
| Forensics vs. analytics | Analytics generates real-time alerts; forensics produces Daubert-standard reports with chain-of-custody logs for court use. |
| Key tools | Commercial platforms (Chainalysis, TRM Labs, Elliptic) lead on evidence readiness; open-source tools (Wachi, Chainmap, DeepLens) support triage. |
| Primary limits | Mixers, privacy coins, cross-chain bridges, and false attribution labels can frustrate tracing and require off-chain corroboration. |
| Murphyslawcrypto | Combines forensic investigation with active litigation, handling evidence preservation, subpoenas, and courtroom recovery for fraud victims. |
Table of Contents
- Who uses on-chain forensics and what can it actually accomplish?
- How does on-chain forensics differ from general blockchain analytics?
- What does an on-chain forensic investigation actually look like?
- Which tools do investigators actually use?
- Real-world cases where on-chain forensics made the difference
- What makes on-chain forensic evidence admissible in U.S. proceedings?
- What are the real limits of on-chain forensics?
- When should you contact a lawyer or a forensic specialist?
- The gap between a forensic report and a litigation strategy
- Murphyslawcrypto handles the full forensic-to-litigation pipeline
- Sources
- FAQ
Who uses on-chain forensics and what can it actually accomplish?
The discipline serves a wide range of professionals, each with a different goal:
- Law enforcement and federal prosecutors tracing ransomware payments, darknet market proceeds, or exchange hacks
- Compliance teams and exchanges running AML/KYC screening and OFAC sanctions checks on wallet addresses
- Auditors validating proof-of-reserves, detecting wash trading, and identifying suspicious wallet activity, as Blockchain Council documents
- Fraud victims and their attorneys building asset-tracing evidence for civil recovery or class action litigation
- Security incident response teams scoping the damage from a DeFi exploit or exchange breach
- Regulators building enforcement records, as demonstrated by SEC enforcement actions that relied on blockchain intelligence
Two realistic outcomes illustrate what the process can deliver. A compliance team that flags a sanctioned wallet address can freeze an outbound transfer before it settles, provided the exchange cooperates quickly. An attorney who commissions a full forensic report can attach a chain-of-custody-verified transaction graph to a civil complaint, supporting a subpoena for KYC records from the receiving exchange. Cross-sector collaboration among exchanges, law firms, and forensic vendors is what makes both outcomes possible.
How does on-chain forensics differ from general blockchain analytics?
The distinction matters because it determines what you can do with the output.
| Dimension | Blockchain Analytics | On-Chain Forensics |
|---|---|---|
| Primary purpose | Real-time monitoring, risk scoring, alerts | Evidence production for legal or regulatory proceedings |
| Typical audience | Compliance teams, exchanges, risk officers | Law enforcement, litigators, forensic examiners |
| Evidentiary standard | Internal risk threshold | Daubert-standard methodology, reproducible steps |
| Output | Dashboards, automated alerts, risk scores | Forensic report, chain-of-custody log, expert affidavit |
| Data retention | Vendor-managed, often aggregated | Preserved raw exports, hash-verified, timestamped |
A practical escalation path looks like this: an analytics platform flags an incoming deposit as high-risk because the sending address clusters with known mixer activity. That alert triggers a compliance hold. The compliance team then commissions a forensic investigation, which collects raw node data, documents every analytical step, and produces a report that can accompany a subpoena or support a regulatory filing. The analytics system generated the lead; the forensic investigation built the case. Cointegrity’s definition of on-chain forensics captures this distinction well, emphasizing cryptographic verification, temporal pattern matching, and the combination of on-chain with off-chain intelligence as the markers of the forensic tier.
What does an on-chain forensic investigation actually look like?
The process is reproducible and follows a defined sequence. Here is the practitioner workflow:
- Scoping and hypothesis formation. Define the incident: what addresses are known, what time window is relevant, what blockchain networks are in scope, and what the investigative goal is (identify a perpetrator, trace cashout, support a subpoena).
- Data collection. Pull raw transaction data from full nodes, archive nodes, or RPC endpoints rather than relying solely on block explorers. Explorer data can have gaps; node-level exports are more complete and easier to hash-verify.
- Address clustering and linkage. Apply heuristics (common input ownership, change address detection, deposit address reuse) to group addresses likely controlled by the same entity. This is where the investigator builds a map of the suspect’s wallet cluster.
- Entity attribution. Match clusters to known entities using OSINT, exchange deposit address mappings, published attribution databases, and off-chain records. A cluster linked to a named exchange becomes an actionable lead for a subpoena.
- Transaction graph analysis and cross-chain tracing. Follow fund flows across hops, through bridges, and across chains. Cross-chain tracing is technically demanding because each chain has its own data format and bridge contracts introduce attribution gaps.
- Reporting and chain-of-custody documentation. Produce a written report that documents methodology, data sources, confidence levels, and every analytical step in reproducible order. Attach hash-verified exports and a qualified examiner’s sign-off.
Pro Tip: Archive your raw data exports at the moment of collection and record the node endpoint, block height, and timestamp. A hash of the export file, logged before any analysis begins, is what allows a court to verify the data was not altered after the fact. This single step is what separates a usable forensic exhibit from a contested one.
A short trace example illustrates the logic. An attacker drains a DeFi protocol from Address A. The funds move through three intermediate addresses (B, C, D) in rapid succession, a pattern consistent with peel-chain laundering. Address D deposits to a centralized exchange. The investigator identifies the exchange from its known deposit address range, documents the hop sequence with timestamps and transaction hashes, and submits a subpoena for the KYC records tied to that deposit address. The Wachi open-source tool can automate much of this triage, converting a transaction hash into a forensic-style REPORT.md that covers fund flow, contract detection, and recursive funding origin tracing.
Which tools do investigators actually use?
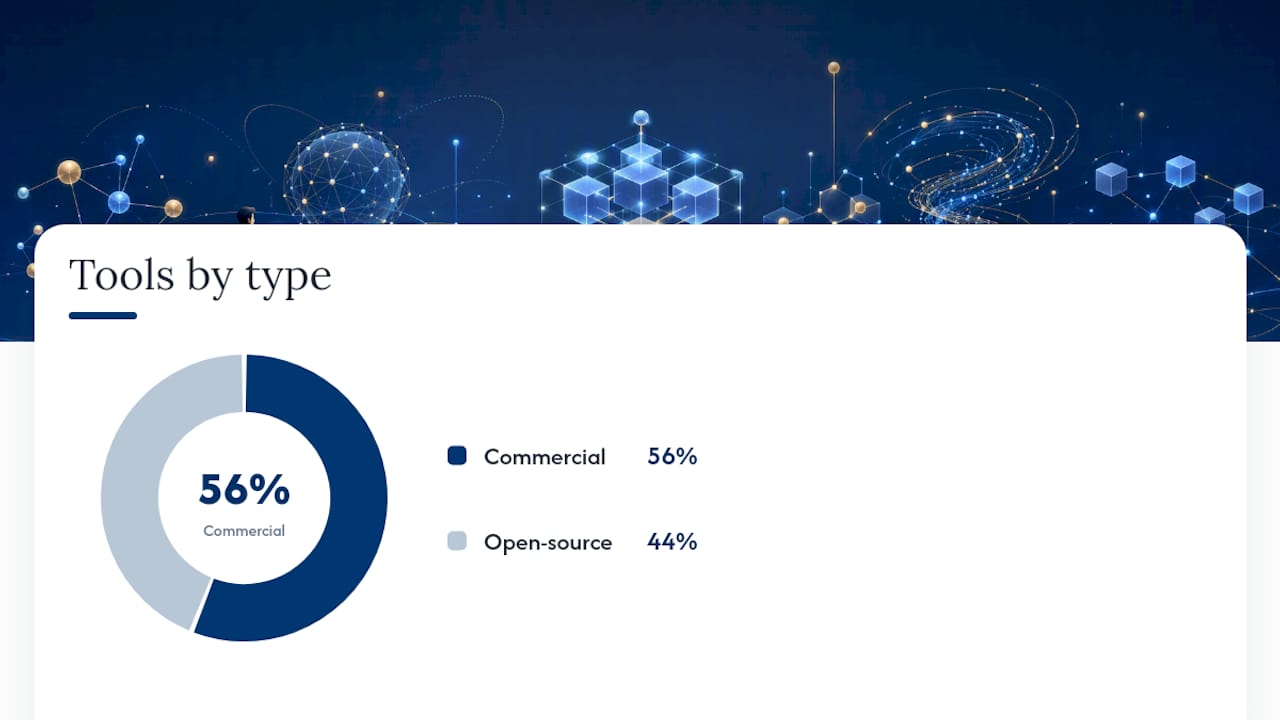
Commercial platforms and open-source tools serve different parts of the workflow. The named platforms below appear regularly in forensic reports and vendor proposals.
Commercial intelligence platforms provide the broadest attribution databases, automated clustering, and court-ready report generation. They are the standard choice for law enforcement and large compliance programs.
- Chainalysis is the most widely cited platform in U.S. enforcement contexts, offering transaction tracing, entity attribution, and documented methodology that has supported prosecutions.
- TRM Labs focuses on financial crime intelligence with multichain coverage and risk scoring used by banks and exchanges.
- Elliptic combines transaction monitoring with sanctions screening and is used by financial institutions for AML compliance.
- Merkle Science offers predictive risk scoring and compliance monitoring, with particular depth in DeFi and emerging chain coverage.
- Scorechain provides AML compliance and transaction monitoring with a focus on European regulatory requirements, though it is available to U.S. teams as well.
Open-source and local tools are increasingly capable for triage and education, and they keep investigator data local, which matters for privilege and confidentiality.
- Etherscan is the standard block explorer for Ethereum and EVM chains, used for quick address lookups and transaction verification. It is a starting point, not a forensic platform on its own.
- Wachi is an OSINT tool that produces a forensic-style report from a transaction hash, covering fund flow, contract profiling, and funding origin traces, as shown in its GitHub repository.
- Chainmap uses the Etherscan v2 API to draw directed address-to-address graphs with peel-chain detection, sink/faucet detection, and calldata decoding, all client-side so API keys and data stay local, per its GitHub repository.
- DeepLens is a desktop application for EVM networks that runs entirely locally, supporting address profiling, entity grouping, and path analysis with hop sequences, role classification, and composite path scoring.
| Platform | Primary use | Evidence readiness | Chains supported | Technical depth | Open-source vs. commercial |
|---|---|---|---|---|---|
| Chainalysis | Investigations, compliance | High — documented methodology, court use | Multichain, broad | Full API and UI | Commercial |
| TRM Labs | Financial crime, AML | High — risk scoring, reporting | Multichain | API and UI | Commercial |
| Elliptic | AML, sanctions screening | High — compliance-grade | Multichain | UI-focused | Commercial |
| Merkle Science | DeFi compliance, monitoring | Medium-high | Multichain, DeFi depth | UI and API | Commercial |
| Scorechain | AML compliance | Medium-high | Major chains | UI-focused | Commercial |
| Etherscan | Quick lookups, verification | Low — explorer only | Ethereum/EVM | Public UI | Free/open |
| Wachi | OSINT triage, report generation | Medium — REPORT.md output | EVM | CLI/API | Open-source |
| Chainmap | Fund-flow visualization | Low-medium — educational, OSINT | EVM multichain | Client-side UI | Open-source |
| DeepLens | Local EVM investigation | Medium — local storage, path scoring | EVM | Desktop app | Open-source |
Real-world cases where on-chain forensics made the difference
These scenarios reflect the types of matters U.S. investigators and attorneys handle regularly.
- Exchange hack. Investigators trace stolen funds from the breach address through a series of hops to deposit addresses at multiple exchanges. Subpoenas to those exchanges yield KYC records that identify the account holders, supporting both criminal referral and civil asset freeze.
- DeFi exploit. A flash loan attack drains a protocol. On-chain forensics maps the attacker’s contract calls, identifies the funding source (often a prior address with exchange history), and documents the profit extraction path. The Wachi tool was demonstrated on a real DeFi exploit example showing approximate damage and attacker profit.
- Ransomware payment tracing. A business pays a ransom in Bitcoin. Investigators trace the payment through mixing hops and identify a cashout address at a regulated exchange, enabling law enforcement to issue a legal process request.
- Wash trading detection. Auditors use on-chain data to identify circular trading patterns between wallets controlled by the same entity, supporting fraud findings in an enforcement context.
- Proof-of-reserves audit. An exchange claims to hold customer funds. Auditors cross-reference on-chain balances against reported holdings, flagging discrepancies that indicate commingling or shortfalls.
In U.S. contexts, the typical timeline from incident to exchange cooperation runs several weeks to several months, depending on whether the receiving exchange is domestic or foreign, whether a subpoena is required, and how quickly law enforcement engages. Domestic exchanges generally respond faster to legal process than offshore platforms.
What makes on-chain forensic evidence admissible in U.S. proceedings?
Courts do not automatically accept blockchain data as evidence. Admissibility depends on how the evidence was collected, documented, and presented. A checklist for evidence preservation:
- Preserve raw data exports at the time of collection, before any analysis
- Document the node endpoint, block height, and exact timestamp for each export
- Generate and log a cryptographic hash of every export file immediately after collection
- Maintain a chain-of-custody log that records every person who accessed the data and every tool applied to it
- Use reproducible analytical steps that a second examiner could independently replicate
- Have a qualified forensic examiner review and sign off on the methodology
- Produce a written report that states confidence levels and distinguishes inference from confirmed attribution
Daubert-standard relevance requires that the methodology be testable, peer-reviewed or widely accepted, and applied consistently. OFAC sanctions screening results and exchange cooperation records strengthen the evidentiary record by adding off-chain corroboration. Courts expect a forensic report to explain not just what the investigator found, but how, and why the analytical method is reliable. An expert affidavit from the examiner is standard in both civil and criminal matters. For a practical guide to preserving evidence from the moment of loss, see Murphy’s Law’s victim evidence guide.
Understanding why crypto scams are hard to prosecute is also relevant here: evidentiary gaps, offshore actors, and pseudonymous addresses all create obstacles that a well-documented forensic report is designed to overcome.
What are the real limits of on-chain forensics?
On-chain forensics is powerful, but it has defined limits that every investigator and attorney should understand before drawing conclusions.
- Pseudonymity, not anonymity. Blockchain addresses are pseudonymous. Attribution requires linking an address to a real-world identity through off-chain data, and that link can be challenged.
- Mixers and tumblers. Services like coin mixers deliberately break transaction linkage. Investigators can often identify mixer use and flag it, but tracing through a well-used mixer to a specific output address is technically difficult.
- Privacy coins. Monero and similar protocols use cryptographic techniques that make transaction tracing substantially harder or, in some cases, currently infeasible.
- Cross-chain bridges. Moving funds across chains through a bridge creates an attribution gap. The investigator must correlate bridge deposit and withdrawal events, which requires data from multiple chains and bridge contract logs.
- False labels and spoofing. Attribution databases can contain incorrect or outdated entity labels. An address labeled as belonging to a known exchange may have been reassigned or may have been incorrectly tagged.
- Explorer data gaps. Public block explorers may not index all transaction types or may have rate limits that affect data completeness. Node-level data is more reliable for forensic purposes.
Common evasion techniques and their mitigations: chain hopping through multiple bridges slows tracing but leaves cross-chain event logs that a skilled investigator can correlate. OTC and peer-to-peer trades attempt to avoid exchange KYC, but large cash-out volumes often still touch regulated on-ramps. Identity obfuscation through multiple layers of wallets increases investigative complexity but rarely eliminates all linkage.
On-chain inference alone is rarely sufficient. Corroborating on-chain findings with off-chain data, such as IP logs, KYC records, and communications, is what converts a strong investigative hypothesis into admissible evidence.
When should you contact a lawyer or a forensic specialist?
Some situations call for immediate professional involvement rather than self-directed investigation.
- You have lost a material amount of funds to theft, fraud, or an exploit
- You have received a ransom demand or an extortion threat involving cryptocurrency
- You have reason to believe criminal conduct occurred (fraud, market manipulation, unauthorized access)
- You are facing a regulatory inquiry or enforcement action that involves transaction records
- You need a subpoena, a freeze order, or emergency injunctive relief to preserve assets
- You are a business that has suffered a breach and needs to notify regulators or affected users
- You need a forensic report that will be used in litigation or submitted to a court
When evaluating a forensic provider or legal team, ask specifically: Have they produced reports that have been admitted in U.S. federal or state court? Can they describe their chain-of-custody process in detail? Have they provided expert testimony under the Daubert standard? Can they show examples of multichain tracing across bridges and privacy-enhanced protocols? What is their process for coordinating with exchanges on subpoena responses?
A combined legal and forensic engagement typically begins with evidence preservation, moves to forensic analysis and report production, and then proceeds to legal action, whether that is a civil complaint, a criminal referral, or a regulatory filing. For victims, the legal options for recovering stolen cryptocurrency include civil litigation, exchange cooperation requests, and law enforcement referrals, each with different timelines and cost structures.
The gap between a forensic report and a litigation strategy
Most on-chain forensic tools are built by technologists, not litigators. The output, however accurate, still needs to be translated into a legal theory, attached to the right procedural vehicle, and defended under cross-examination. A forensic report that identifies a cashout address at a U.S. exchange is a lead, not a recovery. Converting that lead into a freeze order, a judgment, or a settlement requires counsel who understands both the technical evidence and the litigation mechanics.
The firms that handle these matters most effectively are the ones where the forensic analyst and the litigator are working from the same case theory from day one, not handing off a report across a wall. That integration is what determines whether a technically sound forensic finding actually produces a recovery for the client.
Murphyslawcrypto handles the full forensic-to-litigation pipeline
Murphyslawcrypto, founded by Liam Murphy, Esq. (Penn Law, formerly Paul Hastings, Selendy Gay, and McKool Smith), is a licensed crypto law firm that combines forensic-grade blockchain investigation with active courtroom litigation. The firm has litigated matters involving Celsius, Terraform Labs, and BitMEX, and maintains a current docket of fraud and recovery cases. Unlike unregulated “crypto recovery services,” Murphyslawcrypto can preserve evidence, coordinate forensic analysis, issue subpoenas, negotiate with exchanges, and take a case to trial. If you have suffered a loss or are facing a regulatory inquiry, the practical next step is to explore your legal recovery options or review the firm’s full range of litigation and compliance services before the evidence window closes.
Sources
- What Is Blockchain Forensics? Definition, Process & Daubert Standard – Chainalysis
- On-chain Forensics — Web3 Glossary Definition | Cointegrity
- Wachi — GitHub repository
- chainmap — GitHub repository
- SEC press release (2023-59)
This article is general information, not a substitute for advice from a qualified lawyer. Consult a qualified legal professional about your own circumstances before acting on anything here.
FAQ
What is on-chain forensics in plain terms?
On-chain forensics is the structured process of tracing cryptocurrency transactions on a public blockchain to produce evidence for investigations, litigation, or regulatory compliance. It goes beyond simple lookups by applying clustering, attribution, and chain-of-custody documentation to meet legal evidentiary standards.
What does Chainalysis actually do?
Chainalysis is a commercial blockchain intelligence platform that traces illicit funds, attributes wallet addresses to known entities, and produces court-ready forensic reports used by law enforcement and financial institutions in the U.S. and globally.
Can on-chain forensics recover stolen crypto?
Forensics alone does not recover funds. It identifies where stolen assets moved and who likely controls the receiving addresses, which then supports legal action such as a subpoena, a civil freeze order, or a criminal referral that can lead to recovery.
What is the difference between on-chain forensics and blockchain analytics?
Blockchain analytics focuses on real-time monitoring and risk scoring; on-chain forensics produces documented, reproducible evidence suitable for court proceedings, including chain-of-custody logs and expert affidavits that meet the Daubert standard.
When should a fraud victim hire a crypto lawyer instead of a forensic tool?
If you have suffered a material loss, need a subpoena or freeze order, or face a regulatory inquiry, you need legal counsel, not just a tool. A lawyer can use forensic findings as the basis for litigation, exchange cooperation requests, and asset recovery actions that no software platform can initiate on its own.